Commercial-Enterprise-Icon

Commercial Enterprise

Enterprise Network Segmentation with Zero Trust Microsegmentation

Elisity helps enterprises contain lateral movement across users, devices and workloads, including those running AI agents. Build policy from identity and risk context, simulate changes against observed traffic, and enforce least-privilege access through supported network infrastructure.
Download Solution Brief
Manufacturing_Shipping_Gradient_Image

Challenges

Enterprise organizations with complex physical and digital infrastructures struggle to secure diverse networks, prevent lateral movement attacks, and maintain operational continuity while meeting compliance requirements. Traditional zero trust microsegmentation and network segmentation approaches often create more problems than they solve.
Network Segmentation Without Compromise

Transform network security with identity-based microsegmentation that enables Zero Trust in weeks, not years.

Expanded Attack Surface

Digital transformation initiatives have connected previously isolated operational systems with enterprise networks, creating an expanded attack surface where a single compromised endpoint can lead to widespread disruption.

Down_arrow
challenge-solution_icon

Unified Network Visibility

Elisity IdentityGraph combines network observations with context from identity, endpoint, CMDB, IoT and cloud tools. Teams use one correlated asset record to build policy across managed and unmanaged devices and workloads.

Diverse Device Ecosystem

Modern enterprises manage an increasingly diverse ecosystem of devices—from operational systems to IoT sensors to employee devices—many of which cannot be secured with traditional endpoint protection solutions.

Down_arrow
challenge-solution_icon

Simplified Zero Trust Implementation

Use supported network infrastructure to enforce identity-based policy without installing software agents on the assets being protected. Check hardware and software compatibility, then simulate policy before activation.

Operational Continuity Requirements

Organizations cannot tolerate the downtime or disruption that traditional security implementations often require, creating resistance to implementing proper security controls.

Down_arrow
challenge-solution_icon

Automated Policy Management

Leverage Elisity's policy simulation capabilities to simulate, refine, and implement security policies that protect critical systems from lateral movement attacks while enabling authorized business communications across your enterprise.

Compliance Complexity

Meeting regulatory requirements across different business units becomes increasingly challenging with traditional network segmentation approaches that rely on complex VLAN configurations and hardware deployments.

Down_arrow
challenge-solution_icon

Scalable Security Architecture

Roll out reviewed policies by site, business unit or asset group. Use observed traffic to evaluate the next change and refine access as the environment changes.

See It In Action

Put Workload Context to Work

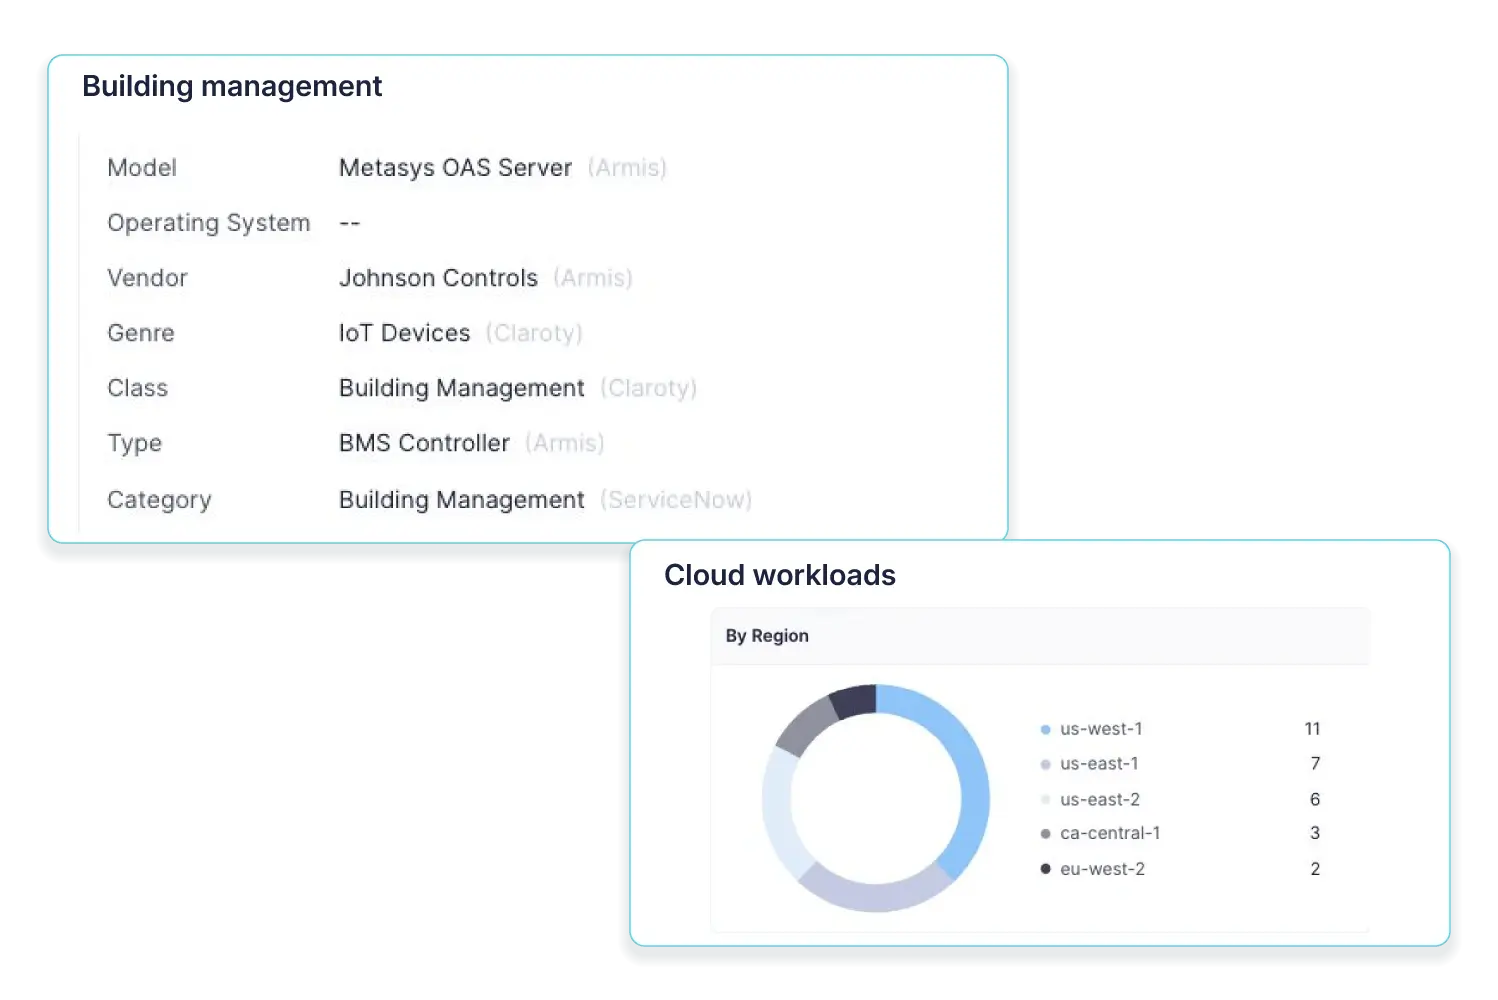
Bring cloud workload tags and instance details into IdentityGraph alongside users and devices. Apply network policy to the device or workload hosting an AI agent.

Elisity identity context for a building-management controller alongside cloud workloads by region.
Get_Start_Eyebrow

Stop East-West Attacks, Microsegment Your Networks

Learn why and how large enterprises are reducing risks and accelerating their Zero Trust maturity with Elisity. 
Learn More

Resources


Elisity Microsegmentation: Accelerate Zero Trust Security in Weeks, Not Years

Download and discover a leap forward in network segmentation architecture.

Enterprise Network Segmentation FAQ

Enterprise environments are complex — Elisity makes securing them simple. Check out these FAQs to learn how we help global organizations enforce zero trust microsegmentation across every user, workload, device and site.
How does Elisity use the network infrastructure we already have?

Elisity programs identity-based policy into supported network infrastructure. Virtual Edge operates outside the data path, and protected devices do not need an Elisity endpoint agent. Check the current hardware and software compatibility guidance before planning a deployment.

How can we review a policy before activating it?

Use simulation to assess a proposed policy against observed traffic. Administrators review the results, refine access and decide which policies move to enforcement. Simulation supports review; it does not guarantee that a change cannot affect operations.

How does Elisity help protect AI agents and workloads?

Elisity applies network access policy to the device or workload running an AI agent, whether that host is an employee computer or a workload in a supported environment. Enforcement takes place through the network, outside the agent’s runtime. Additional service-account and machine-credential identity support is in development.

Back to top

Resources

EO 14412: the post-quantum cryptography executive order
Overhead dusk aerial of a federal government district: limestone courtyard buildings, a diagonal avenue and light trails

EO 14412: the post-quantum cryptography executive order

18 min read
Post-Quantum Cryptography Vendors in 2026: Who Does What, by Migration Stage
Security architect sorting color-coded cards into five columns on a glass wall, mapping a post-quantum migration

Post-Quantum Cryptography Vendors in 2026: Who Does What, by Migration Stage

19 min read
How to Protect Systems That Can’t Be Upgraded to Post-Quantum Cryptography
Overhead view of a manufacturing plant roof with rooftop units and skylights and a row of trailers at the docks, in a blue-teal grade

How to Protect Systems That Can’t Be Upgraded to Post-Quantum Cryptography

19 min read

Ready to Prevent Lateral Movement?​ Secure Your Network in Weeks, Not Years

Don't wait for attackers to exploit your east-west traffic security policy gaps. Implement Elisity's identity-based microsegmentation without agents, hardware, or network changes. Discover 99% of all users, workloads, and devices in one day, create dynamic least privilege policies, and prevent lateral movement—all while leveraging your existing infrastructure. Schedule your personalized demo today.​
Elisity_White