Use Case


Network Visibility

Elisity IdentityGraph combines network observations with identity, endpoint, CMDB, IoT and cloud context in one correlated record per asset. Use that context to build Policy Groups and least-privilege access for users, devices and workloads, including those running AI agents.

AWS and Azure connectors bring workload inventory, cloud tags and instance details into IdentityGraph. Elisity applies network access policy to the device or workload hosting an AI agent, outside the agent’s runtime. Additional service-account and machine-credential identity support is in development.

Challenges

Today's enterprises struggle with fragmented network visibility tools and disparate security tools, complex infrastructure, and siloed teams. Security leaders face mounting operational costs from deploying agents, hardware sensors, and network taps while still lacking a unified view of their attack surface. This fragmentation leaves dangerous blind spots that attackers can exploit.

Environment_Gradient_2

Network Segmentation Without Compromise

Transform network security with identity-based microsegmentation that enables Zero Trust in weeks, not years.

Challenge


Fragmented Tools & Data Security

Teams waste valuable time correlating data between multiple monitoring tools and platforms, creating delays in threat detection and incident response

Down_arrow
challenge-solution_icon

Elisity Solution


Unified Discovery & Intelligence

Elisity IdentityGraph correlates network observations with identity, endpoint, CMDB, IoT and cloud context. Bring discovered users, devices and workloads into one asset view to support policy decisions.

Challenge


Manual Asset Discovery

Traditional methods require extensive manual effort to track and classify devices, leaving organizations vulnerable to unmanaged and shadow IT assets.

Down_arrow
challenge-solution_icon

Elisity Solution


Automated Asset Classification

The platform continuously monitors and auto-classifies all managed and unmanaged assets, leveraging metadata from your existing infrastructure and security stack.

Challenge


High Operational Costs

Organizations invest heavily in agents, hardware sensors, and dedicated staff to maintain network visibility solutions, yet still struggle with blind spots across their infrastructure.

Down_arrow
challenge-solution_icon

Elisity Solution


Frictionless Deployment

Deploy in days using your existing network infrastructure - no agents, new hardware, or network changes required. Get immediate visibility into your complete attack surface.

See

Connect asset identity and workload context

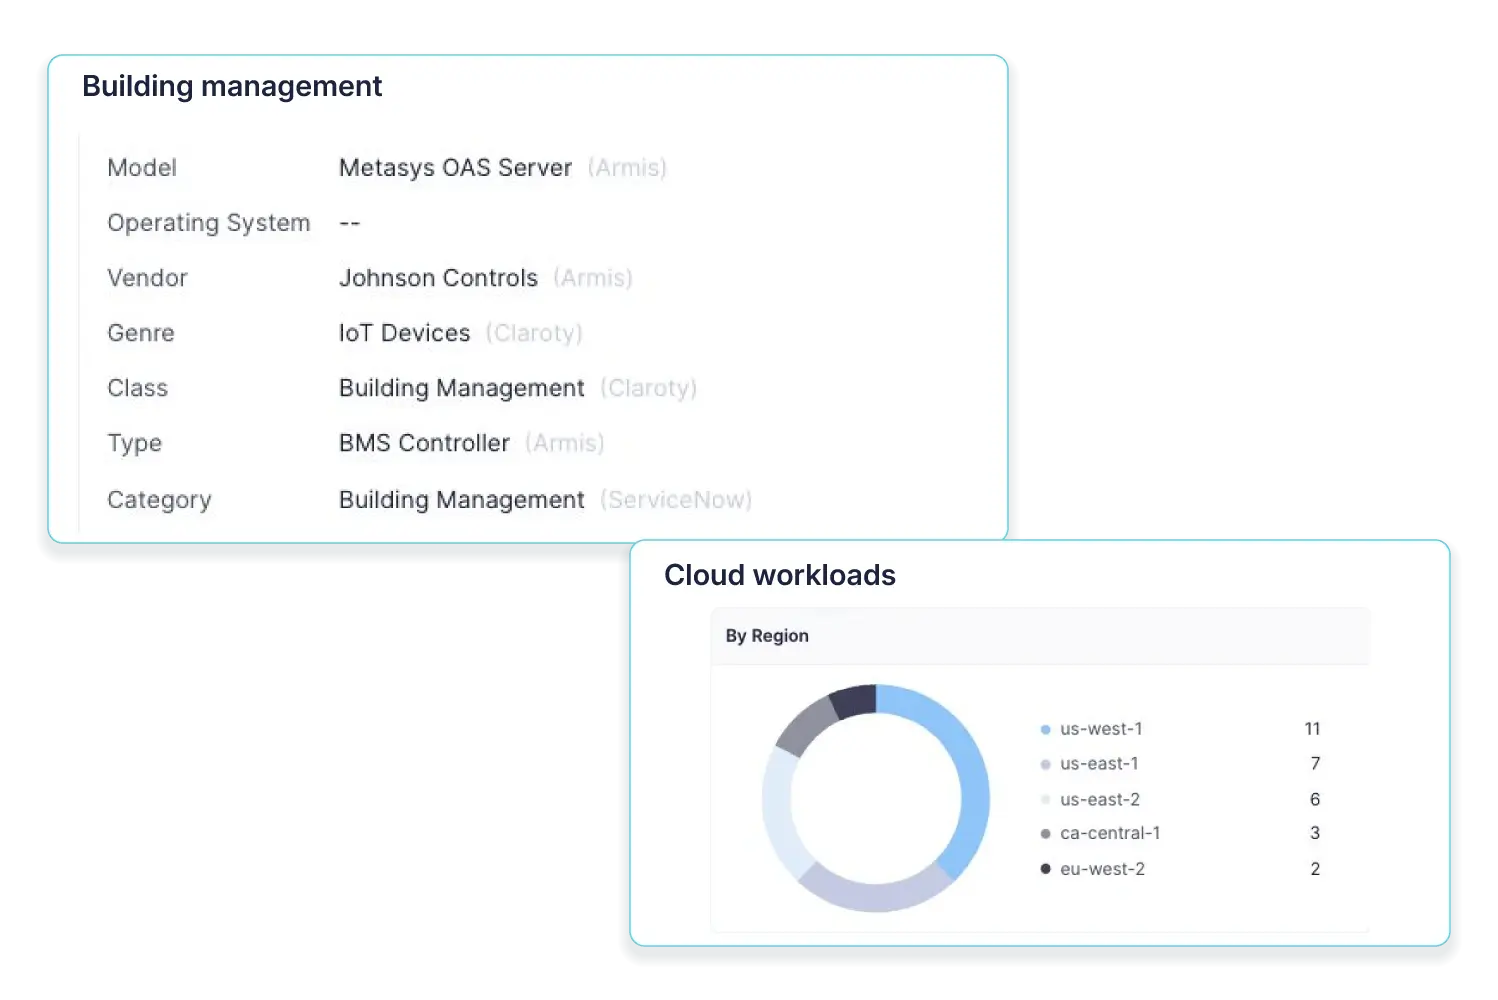
Elisity IdentityGraph combines network observations with connected sources. Bring device attributes and cloud workload context together to build identity-based policy.

Elisity identity context for a building-management controller alongside cloud workloads by region.

Resources


Elisity Microsegmentation: Accelerate Zero Trust Security in Weeks, Not Years

Download and discover a leap forward in network segmentation architecture.
Get_Start_Eyebrow

Stop East-West Attacks, Microsegment Your Networks

Learn why and how large enterprises are reducing risks and accelerating their Zero Trust maturity with Elisity. 
Learn More

Network Visibility FAQ

Struggling with blind spots and fragmented tools? These FAQs explain how Elisity delivers unified, real-time visibility across your entire network without adding complexity.

How does Elisity provide a unified view of network activity across all users and devices?

Elisity automatically discovers and correlates all users, workloads, and devices into a single, unified dashboard. Instead of jumping between tools, you can see all assets and traffic patterns clearly, helping you quickly identify anomalies and vulnerabilities.

We're using multiple monitoring tools but still have blind spots—can Elisity help?

Elisity eliminates visibility gaps by continuously monitoring all assets, managed or unmanaged, and classifying them automatically. Consolidating multiple siloed tools into one platform reduces blind spots and enhances security efficiency.

Can we gain comprehensive network visibility without deploying agents or tapping every network segment?

Yes, Elisity provides agentless visibility using your existing infrastructure, transforming the network edge into security sensors. This method ensures visibility across your network with minimal effort and zero performance impact.

How quickly can Elisity improve our visibility after deployment?

Elisity can provide comprehensive network visibility within days. Since it doesn't require hardware or complex integrations, you quickly gain critical insight into assets and traffic, immediately improving your security posture.

Back to top
How to Protect Systems That Can’t Be Upgraded to Post-Quantum Cryptography
Overhead view of a manufacturing plant roof with rooftop units and skylights and a row of trailers at the docks, in a blue-teal grade

How to Protect Systems That Can’t Be Upgraded to Post-Quantum Cryptography

14 min read
Cybersecurity Budget 2027: Benchmarks, Priorities and Business Case
Aerial view straight down on data center halls with rows of rooftop cooling units, in a cool blue-teal gradient

Cybersecurity Budget 2027: Benchmarks, Priorities and Business Case

27 min read
The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story
Overhead aerial of a data center campus under construction in farmland, illustrating AI agent containment architecture

The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story

14 min read
See Elisity on your network

See how Elisity builds policy from identity and context, simulates changes against observed traffic, and enforces least-privilege access through supported network infrastructure. Schedule a demo for your environment.
Elisity_White