Healthcare-Institutions_Icon

BioTech and Pharma

Pharmaceutical and BioTech Network Segmentation with Manufacturing System Microsegmentation

Pharmaceutical and biotech environments connect drug discovery, clinical trials and production systems. Elisity helps teams limit lateral movement through identity-based microsegmentation, review changes before enforcement, and retain segmentation evidence for security and compliance reviews.

Challenges

Pharmaceutical and biotech organizations with multiple manufacturing sites, R&D facilities, and global supply chains face unprecedented security challenges as operational technology (OT) systems connect to enterprise networks. Traditional network segmentation approaches cannot protect these highly regulated environments without risking production downtime or compromising Good Manufacturing Practices (GMP).

People-Shapes-51
Small_Logo
GSK-customer-spotlight-image-1

Customer Spotlight

“Elisity’s deployment at GSK is nothing short of revolutionary, making every other solution pale in comparison.”

— Michael Elmore, CISO, GSK

Network Segmentation Without Compromise

Transform network security with identity-based microsegmentation that enables Zero Trust in weeks, not years.

The Numbers

Main Line Health deploys Elisity microsegmentation enterprise-wide across their Cisco infrastructure with Armis integration, providing comprehensive protection at every facility with network presence.

270+

Actively Enforced Policies

302,000

Devices Protected by Microsegmentation Policies

110

Gloabl Sites - Manufacturing, Labs, Orrices

3

GSK launches 3 Elisity-powered sites per week. worldwide.

Challenge

Expanded Manufacturing Attack Surface

The convergence of IT and OT in pharmaceutical manufacturing has created new attack vectors that cybercriminals exploit to steal intellectual property, disrupt production, or compromise drug safety. With thousands of connected devices spanning multiple sites globally, pharmaceutical companies struggle to maintain visibility and control while meeting stringent FDA requirements.​

Down_arrow
challenge-solution_icon

Elisity Solution

Comprehensive Manufacturing Visibility

Elisity IdentityGraph combines network observations with context from connected tools to discover and classify assets such as manufacturing systems, laboratory equipment and building-management controllers. Use identity, device type and risk attributes to review access across the pharmaceutical environment.

Challenge

Legacy OT System Vulnerabilities

Manufacturing equipment and process control systems often run proprietary software with 10-15 year lifecycles, making them impossible to patch without lengthy revalidation. These systems represent critical infrastructure for drug production but remain unprotected by conventional security tools.

Down_arrow
challenge-solution_icon

Elisity Solution

Segmentation controls and audit evidence

Use identity-based Policy Groups to define the communication between manufacturing systems and supporting services. Simulate proposed changes against observed traffic, review their operational impact, and enforce approved policies through supported network infrastructure. Asset context and policy records can support your security, validation and audit processes.

Challenge

Regulatory Compliance Complexity

Meeting FDA cybersecurity guidelines, IEC 62443 requirements, and maintaining GMP compliance while implementing security controls creates operational challenges. Traditional approaches require extensive validation documentation and risk disrupting qualified systems.

Down_arrow
challenge-solution_icon

Elisity Solution

Zero-Disruption Deployment

Deploy pharmaceutical microsegmentation using your existing network infrastructure without new hardware, agents on validated systems, or production downtime—maintaining continuous manufacturing operations critical to drug supply chains.

Frame 427319008

Supply Chain and IP Protection

Pharmaceutical companies cannot tolerate security implementations that risk intellectual property theft or supply chain disruption, creating resistance to implementing proper controls while maintaining global operations across contract manufacturers and research partners.

Down_arrow
challenge-solution_icon

Elisity Solution

Phased Security Implementation

Roll out policies using Elisity's Simulation Mode to analyze impact on manufacturing processes, identify potential issues, and refine controls before enforcement, safeguarding your operations while protecting valuable research and production data.

See

Build policy around industrial asset context

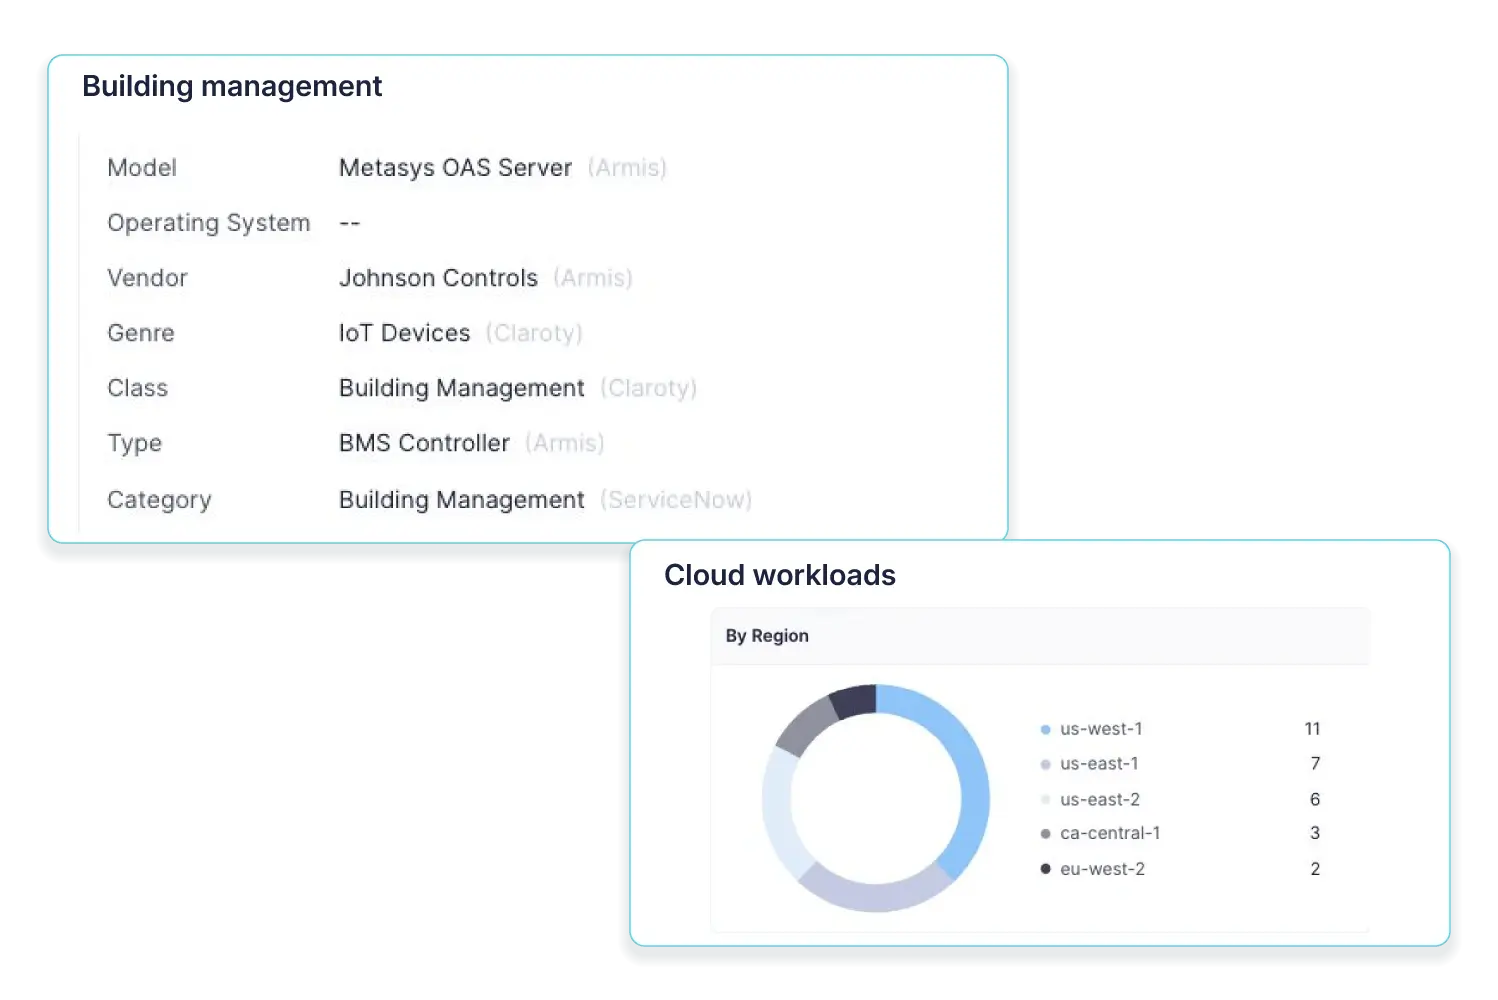
Combine network observations with connected asset and security sources. Use device identity and observed communications to define policy around industrial systems and their supporting workloads.

Elisity identity context for a building-management controller alongside cloud workloads by region.

Resources

Accelerate Zero Trust Security in Weeks, Not Years

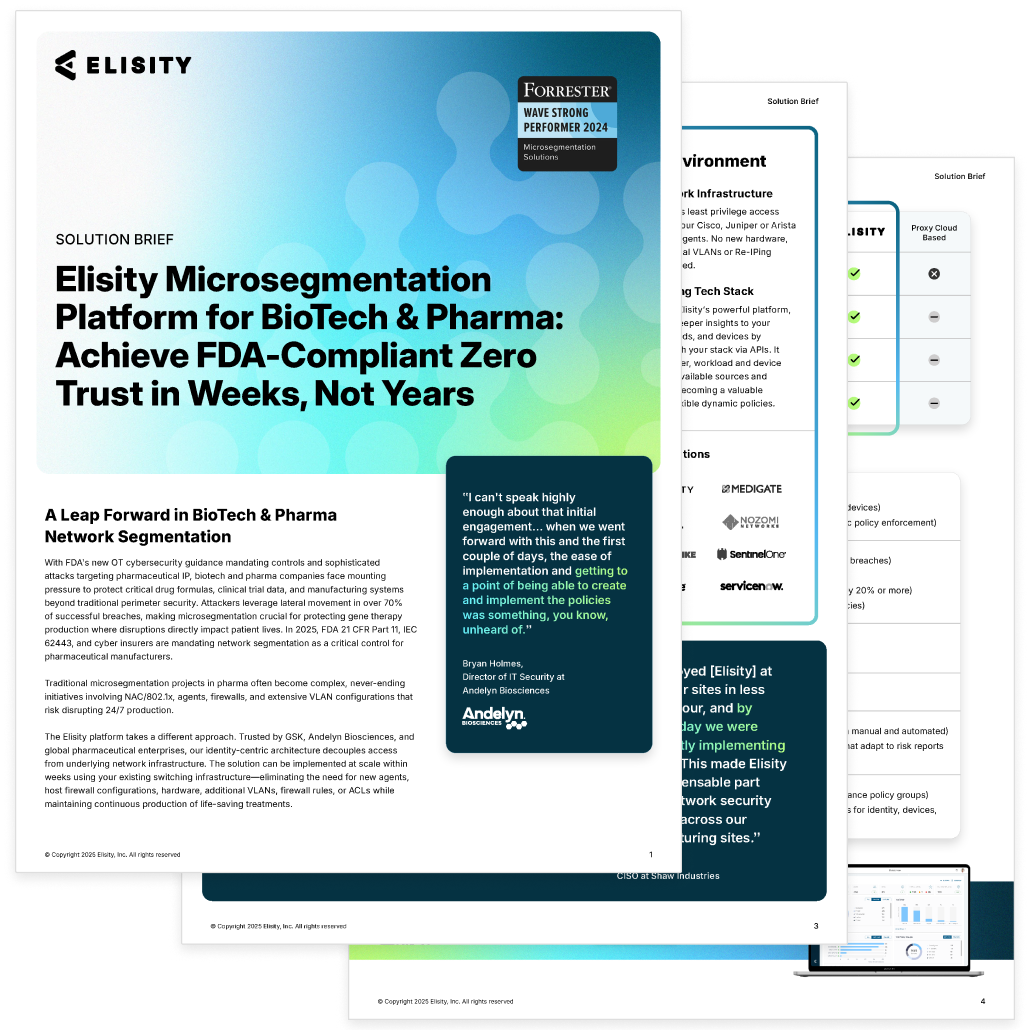
See how GSK reduced microsegmentation costs by 75% while protecting 275 global sites from ransomware and compliance violations. Discover Elisity's identity-based architecture—a leap forward that eliminates the need for new hardware, agents, VLANs, or complex ACLs.

Get the Details
Solution-Brief-Pharma-card-reveal

Get Started

Stop East-West Attacks, Microsegment Your Networks

Learn why and how large enterprises are reducing risks and accelerating their Zero Trust maturity with Elisity. 
Learn More

Pharmaceutical Manufacturing & Biotech Security FAQ

See how Elisity helps pharmaceutical and biotech companies secure manufacturing systems while maintaining compliance and operational continuity. These FAQs answer the most common questions from security and manufacturing teams.


How does Elisity protect pharmaceutical manufacturing systems without requiring downtime?

Elisity's identity-based microsegmentation secures each system at the network level without requiring any software on validated equipment. By limiting communications to only what's necessary for manufacturing processes, it protects critical OT systems from threats.

Does Elisity help with FDA cybersecurity compliance and IEC 62443?

Elisity can support segmentation controls and security reviews through correlated asset context, identity-based policy, simulation and policy records. Teams can use that evidence within their FDA-related, IEC 62443 and other compliance processes. Your organization determines the applicable requirements and validates its control design.

Can we implement this without impacting validated systems?

Absolutely. Elisity's agentless solution uses your existing network infrastructure, allowing you to deploy security policies without any changes to validated systems. You can simulate policies before enforcement to ensure no impact on GMP processes.

How does this simplify our pharmaceutical security operations?

Elisity consolidates OT security into one platform that understands manufacturing contexts. This unified approach means fewer consoles to manage and consistent enforcement across all sites, freeing your team from complex firewall and VLAN management.

Back to top
The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story
Overhead aerial of a data center campus under construction in farmland, illustrating AI agent containment architecture

The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story

14 min read
Elisity Release 26.7: Hierarchical policy, broader platform support, and deeper device context

Elisity Release 26.7: Hierarchical policy, broader platform support, and deeper device context

13 min read
AI Agent Network Security with Microsegmentation
AI agent network security: how microsegmentation contains autonomous AI agents at the network layer

AI Agent Network Security with Microsegmentation

24 min read