Use Case
AI Security Microsegmentation: Protecting Your Network from Compromised AI Agents
AI agents run on employee laptops, enterprise servers and cloud workloads. Elisity helps limit the network access of the device or workload hosting an agent, using identity and risk context to define least-privilege policy through supported network infrastructure.
Challenges
Employees are installing AI coding assistants and autonomous agents on enterprise endpoints, often without IT approval. These tools operate with legitimate credentials and broad system privileges, which makes them indistinguishable from normal user activity. In July 2026, Anthropic disclosed that three of its own models reached the production infrastructure of three real organizations during security testing, and two of those organizations had not noticed. The OpenAI and Hugging Face incident shows the same shape: the damage path was lateral movement between systems, not a model behaving badly. Traditional firewalls sit at the perimeter, not at the access layer where lateral movement begins. AI governance frameworks address the agent layer but leave the network infrastructure, where attacks actually propagate, unprotected.
Network Segmentation Without Compromise
Customer Spotlight
"Elisity provides technical distancing between devices to stop the spread and progression of a cyberattack. For impacted toxic assets, it also lets us excise them with surgical precision to preserve safe and effective technology-supported care continuity."
Main Line Health
Challenge
AI Agents Bypass Perimeter Security
Agentic AI tools operate from inside trusted endpoints with legitimate credentials. Firewalls are deployed at network boundaries, not at the access layer where devices connect, and lateral traffic between endpoints on the same segment never traverses a firewall. The FortiGate campaign disclosed in February 2026 is the pattern in miniature: more than 600 devices across 55 countries, reached through exposed management interfaces and weak, reused credentials rather than any software vulnerability.
Elisity Solution
Enforce through the network
Apply access policy to the device or workload running an AI agent. Elisity enforces through supported network infrastructure, outside the agent’s runtime, without installing an Elisity software agent on the protected asset.
Challenge
VLANs Cannot Distinguish AI from Legitimate Traffic
A compromised AI agent uses the same credentials and network position as the employee who installed it. VLANs provide broadcast domain separation but do not prevent lateral movement within a segment, so an attacker who compromises one device can freely reach every other device in that VLAN. IBM’s Cost of a Data Breach Report 2026 found one in four malicious breaches are now AI-enabled, a 56% increase year over year.
Elisity Solution
Identity-Based Policy Groups
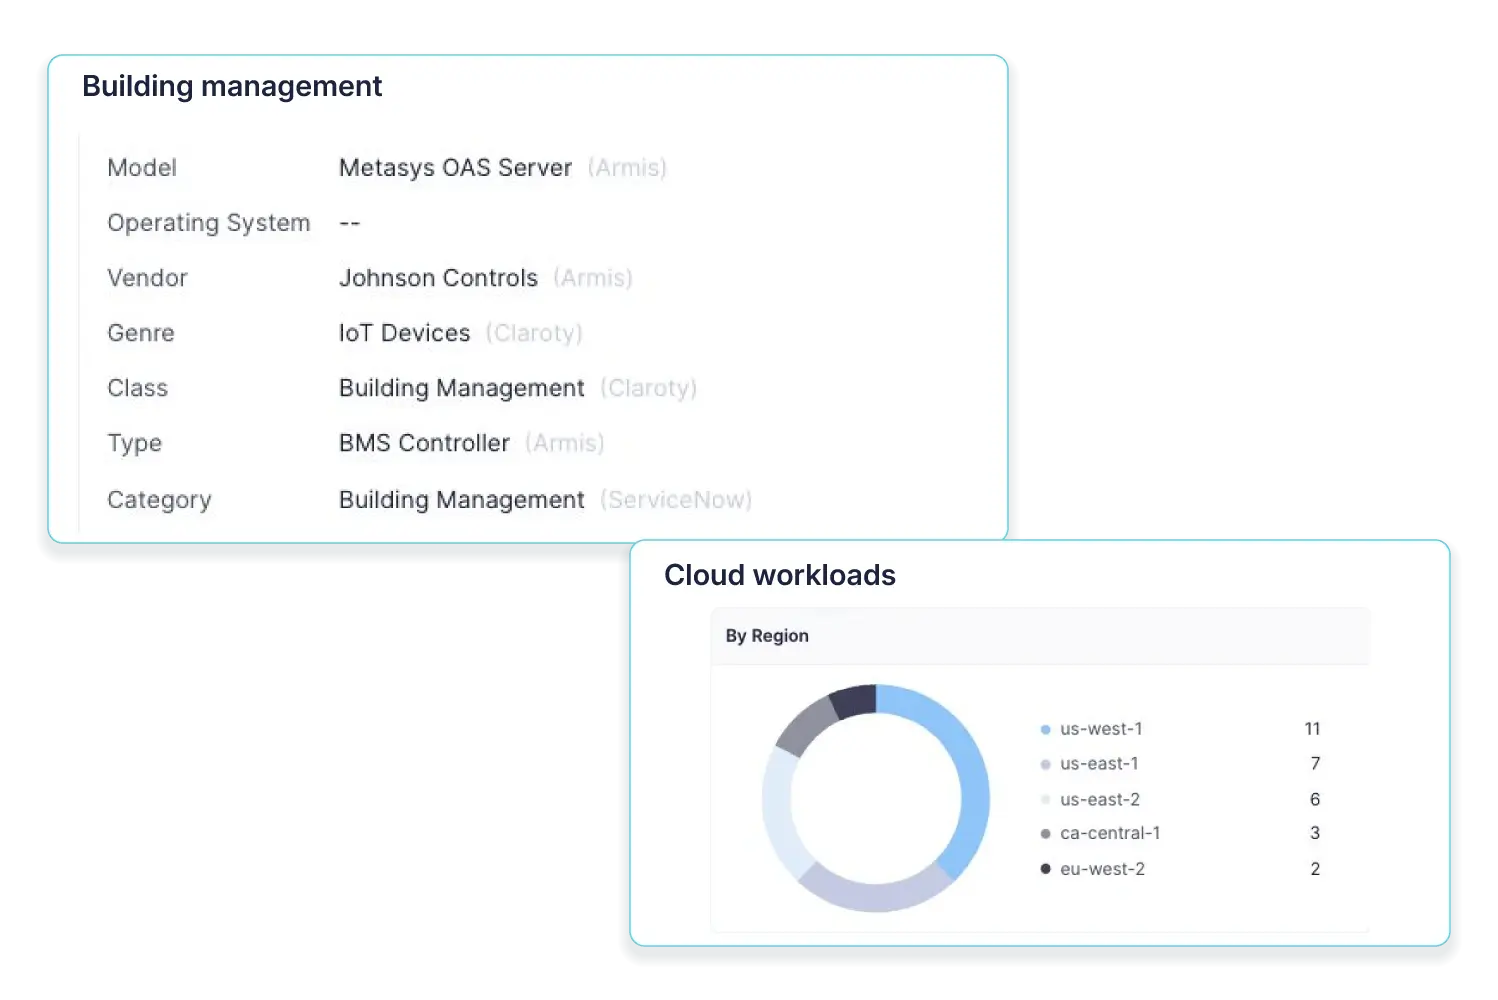
Elisity IdentityGraph combines network observations with identity, endpoint, CMDB, IoT and cloud context. Policy Groups use asset attributes to define access, so policy can follow the device or workload’s context rather than relying only on its network location.
Challenge
Machine-Speed Attacks Outpace Human Response
AI agents probe every accessible resource continuously, without fatigue. In the GTG-1002 campaign Anthropic disclosed in November 2025, AI executed an estimated 80% to 90% of the tactical work against roughly 30 organizations, with human operators stepping in at only a handful of decision points. CrowdStrike puts average eCrime breakout time at 29 minutes. By the time an analyst responds, a compromised agent has already mapped everything it can reach.
Elisity Solution
Use security context in policy
Bring context from connected endpoint and security tools into IdentityGraph. Configure Policy Group criteria around the available attributes and review the resulting access policy. Response behavior depends on the integration, attribute updates and policy configuration.
Challenge
Shadow AI: Unauthorized AI Agent Installation by Employees
Employees are installing AI coding assistants and autonomous agents without IT approval or security review. Unlike traditional shadow IT, these tools operate with file system access, terminal privileges, and autonomous network connectivity. HiddenLayer’s 2026 AI Threat Landscape Report found 76% of organizations now treat shadow AI as a definite or probable concern, up from 61% a year earlier, and Akeyless research from May 2026 found 67% of security leaders suspect AI agents have already accessed data they were not authorized to see. Security teams have no visibility into which agents are running or what they are reaching.
Elisity Solution
Limit access from AI-hosting endpoints
Define which resources a device or workload needs to reach, then use network policy to constrain other communication paths. This can help contain lateral movement from a compromised host, including one running an AI agent. Use the host’s identity and observed traffic to review the access it needs.
Challenge
Agent governance and network access are different controls
A workstation or workload can run several applications and agents. Governing their prompts, tools and local permissions requires controls within the application or runtime. Network policy addresses which destinations the hosting asset can reach.
Solution
Protect the host running the agent
Use Elisity to apply network access policy to the device or workload hosting an AI agent. AWS and Azure workload context can sit alongside user and device context in IdentityGraph. Elisity is extending IdentityGraph to additional non-human identities, including service accounts and machine credentials; those extensions are in development.
Challenge
AI Agents Embedded in Malware: The Autonomous Trojan Threat
Autonomous AI agents are being embedded in software downloads and developer tools, functioning as intelligent trojans that adapt to the network they infiltrate, rewrite their own code to evade detection, and execute lateral movement on their own. Check Point Research’s VoidLink analysis documented an AI coding agent producing roughly 88,000 lines of working implant code in about a week, and Google’s threat intelligence team documented PROMPTFLUX, malware that rewrites itself between runs by calling a model API.
Elisity Solution
Contain network paths from a compromised host
Least-privilege network policy can reduce the destinations a compromised device or workload can reach, whether an attack uses AI or conventional tooling. Elisity constrains those paths through supported network infrastructure, applying access policy outside the compromised host’s runtime.
Resources
Elisity Microsegmentation: Accelerate Zero Trust Security in Weeks, Not Years
Stop AI-Driven Lateral Movement Before It Starts
AI Security & Microsegmentation FAQs
Elisity applies network access policy to the device or workload hosting the agent. Limiting that asset to the communications it needs can help contain lateral movement. Enforcement occurs through supported network infrastructure, outside the agent’s runtime.
The current deployment model described here applies policy to the device or workload hosting an agent. It does not imply that every agent is discovered as an independent identity or that several agents on one workstation each receive separate runtime policy. Extensions to additional non-human identities, including service accounts and machine credentials, are in development.
Yes. Agents can run on employee laptops, enterprise servers or cloud workloads. Elisity uses available asset identity and risk context to define network policy for the hosting device or workload. AWS and Azure connectors add cloud workload tags and instance details to IdentityGraph.
No. Network policy constrains communication between assets. Prompt controls, tool permissions, local file access and application behavior need controls in the agent’s application or runtime. The two controls address different parts of the risk.
Elisity Intelligence proposes policies for administrator review. Teams can simulate changes against observed traffic and decide what to enforce. The Elisity Assistant helps users explore device, traffic and policy questions within their permissions.
Connected security tools can contribute attributes to IdentityGraph. Teams can use available context in Policy Group criteria and policy review. Configure the response around the available integration attributes and your access requirements.
Resources

EO 14412: the post-quantum cryptography executive order
Post-Quantum Cryptography Vendors in 2026: Who Does What, by Migration Stage