Use Case


IoMT Security

Healthcare organizations manage vast networks of IoMT devices across distributed locations, from imaging systems to patient monitoring equipment. Elisity's identity-based microsegmentation platform discovers and secures tens of thousands of devices enterprise-wide, automatically enforcing dynamic security policies based on device identity and risk. This ensures continuous IoMT medical device security and protection of critical systems while maintaining seamless patient care delivery.

Challenges

Healthcare organizations struggle to secure IoMT devices across distributed networks using traditional segmentation approaches. Multiple security tools, siloed teams, and complex manual processes drive up operational costs while creating visibility gaps. With critical patient care networks requiring zero downtime, organizations need a frictionless approach that won't disrupt life-saving medical services.

Place-Healthcare

Network Segmentation Without Compromise

Transform network security with identity-based microsegmentation that enables Zero Trust in weeks, not years.
Small_Logo
MultiCare-customer-spotlight-image

Customer Spotlight


“Elisity gives us the ability to microsegment in a way that’s operationally sustainable and doesn’t add a ton of overhead — and in healthcare, where you simply can’t afford downtime, that’s critical.”

— Jason Elrod, CISO
MultiCare

Challenge


Multiple Tools, Multiple Teams

Healthcare security requires coordinating across clinical engineering, IT, and security teams using different tools and processes to manage IoMT medical devices. This fragmentation creates visibility gaps and security risks.

Down_arrow
challenge-solution_icon

Elisity Challenge


Complete IoMT Visibility & Control

Elisity Cloud Control Center brings medical-device context and network policy into one console, supporting asset visibility and risk-based segmentation. IdentityGraph correlates network observations with connected identity and medical-device tools so teams can review each discovered asset’s communication needs.

Challenge


High Operational Costs

Manual device discovery, classification, and policy management across thousands of IoMT medical devices consumes significant resources while still leaving security gaps in critical networks. Many solutions do not always correlate metadata needed to confidently create policies.

Down_arrow
challenge-solution_icon

Elisity Solution


Segmentation evidence for security reviews

Use asset context, reviewed policies and observed traffic to support medical-device segmentation and security reviews. Connected sources can add risk attributes to IdentityGraph; teams can use those attributes to define Policy Groups and retain policy evidence for their compliance process.

Explore how MDS2 information can inform medical-device security, or review the control patterns in the IoMT segmentation guide.

Challenge


Zero-Downtime Requirements

Critical patient care networks cannot tolerate disruption from security implementations. Traditional segmentation approaches often require network changes that risk impacting life-saving services.

Down_arrow
challenge-solution_icon

Elisity Solution


Clinical-First Security

Elisity implements identity-based microsegmentation without disrupting patient care workflows. Dynamic policies adapt to device risk levels while maintaining continuous operation of critical medical systems.

See

Use medical device context in policy

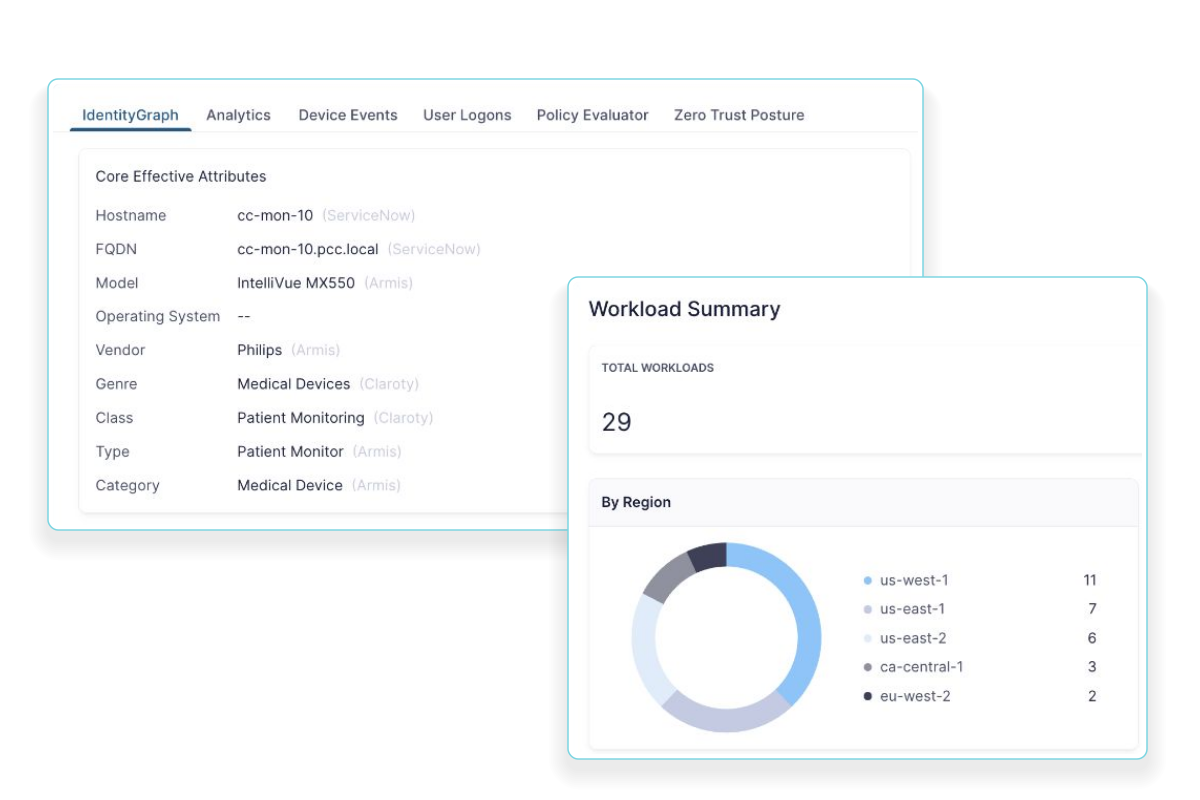
Bring medical device identity and connected asset context into IdentityGraph. Review observed communications before applying segmentation policy through supported network infrastructure.

Elisity IdentityGraph medical-device context alongside a cloud workload summary.

Resources


Elisity Microsegmentation: Accelerate Zero Trust Security in Weeks, Not Years

Download and discover a leap forward in network segmentation architecture.
Get_Start_Eyebrow

Stop East-West Attacks, Microsegment Your Networks

Learn why and how large enterprises are reducing risks and accelerating their Zero Trust maturity with Elisity. 
Learn More

IoMT Security and Segmentation FAQs

Curious how to protect medical devices without risking patient care disruptions? These FAQs dive into how Elisity enables healthcare-ready IoMT medical device security and segmentation that supports compliance and safety.
How can we secure thousands of IoMT devices without disrupting patient care?

Elisity automates IoMT segmentation using dynamic, identity-based policies enforced without network downtime. This ensures critical medical systems are continuously protected without impacting patient care workflows.

Can Elisity help us meet healthcare cybersecurity requirements like HIPAA or HHS 405(d)?

Elisity supports asset visibility, least-privilege network policy and evidence for healthcare security reviews. Teams can use asset context, policy records and observed traffic in their broader risk-management and compliance processes. Applicable requirements and compliance decisions remain organization-specific.

Our IT and clinical teams use separate tools—can Elisity bridge this gap?

Elisity offers a unified Cloud Control Center, providing shared visibility and policies for IoMT devices. This integration reduces miscommunication and enhances consistent security across teams.

IoMT device management is time-consuming and costly—how does Elisity reduce this burden?

Elisity automates device discovery and segmentation, eliminating manual firewall rules or VLAN management. This automation significantly reduces operational costs and frees resources for strategic tasks.

Back to top
The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story
Overhead aerial of a data center campus under construction in farmland, illustrating AI agent containment architecture

The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story

14 min read
Elisity Release 26.7: Hierarchical policy, broader platform support, and deeper device context

Elisity Release 26.7: Hierarchical policy, broader platform support, and deeper device context

13 min read
AI Agent Network Security with Microsegmentation
AI agent network security: how microsegmentation contains autonomous AI agents at the network layer

AI Agent Network Security with Microsegmentation

24 min read
Ready to Prevent Lateral Movement?​ Secure Your Network in Weeks, Not Years

Don't wait for attackers to exploit your east-west traffic security policy gaps. Implement Elisity's identity-based microsegmentation without agents, hardware, or network changes. Discover 99% of all users, workloads, and devices in one day, create dynamic least privilege policies, and prevent lateral movement—all while leveraging your existing infrastructure. Schedule your personalized demo today.​
Elisity_White