Healthcare-Institutions_Icon

Healthcare Institutions
Healthcare Network Segmentation with Medical Device Microsegmentation

Elisity helps healthcare teams contain lateral movement across clinical networks and medical devices. Build least-privilege policy from identity and risk context, simulate changes against observed traffic, and enforce through supported network infrastructure without installing software agents on protected medical devices.

Challenges

Healthcare organizations with 300+ beds, multiple hospitals and clinics face mounting security challenges as legacy medical systems connect to enterprise networks. Traditional network segmentation approaches struggle to protect these complex environments without disrupting critical clinical workflows or requiring expensive infrastructure upgrades.​

Healthcare_institution_employees_at_work
Small_Logo
St-Lukes-customer-spotlight-image

Customer Spotlight

“I remember saying to him in October, ‘Get it done in two months.’ And he delivered two weeks ahead of schedule. That's when the fear went away for me.”

— David Finkelstein, CISO, St. Luke's University Health Network

Network Segmentation Without Compromise

Transform network security with identity-based microsegmentation that enables Zero Trust in weeks, not years.

Case Study Video

15 hospitals. 46 days.

Read the Case Study

The Numbers

St. Luke’s University Health Network segmented 15 hospitals in 46 days using its existing network infrastructure.

85,000

Devices

23,000

Active users

350+

Outpatient sites

0

Change windows

Challenge

Expanded Attack Surface

The proliferation of connected medical and IoT devices has expanded the attack surface across clinical environments, creating new attack vectors that cybercriminals exploit to gain unauthorized access to critical patient care systems and protected health information (PHI). With thousands of devices spanning multiple facilities, healthcare organizations struggle to maintain visibility and control.​

Down_arrow
challenge-solution_icon

Elisity Solution

Comprehensive Healthcare Visibility

Elisity IdentityGraph combines network observations with context from identity, endpoint, CMDB and medical-device tools. Clinical teams can use device classification, ownership and risk attributes to define the communication each discovered asset needs.

Challenge

Legacy Medical Device Vulnerabilities

Clinical devices and IoMT systems often run legacy software, proprietary operating systems, or have long replacement cycles, making them impossible to patch regularly or secure with traditional endpoint solutions. These devices represent a significant portion of a healthcare organization's infrastructure but remain largely unprotected by conventional security tools.​

Down_arrow
challenge-solution_icon

Elisity Solution

Segmentation evidence for compliance reviews

Use identity-based Policy Groups to limit communication between clinical systems. Elisity provides segmentation and policy evidence that can support your compliance review; deploying the platform does not establish compliance by itself.

Challenge

HIPAA Compliance Complexity

Healthcare teams need to understand which systems communicate, why that access is necessary and how policy changes are reviewed. Static rules and fragmented inventories make it harder to maintain and explain those controls.

Down_arrow
challenge-solution_icon

Elisity Solution

Review changes before enforcement

Start with visibility, build policy around clinical communication, and use simulation to assess changes before activation. Roll out administrator-approved policies in phases with the teams responsible for patient care systems.

Frame 427319008

Clinical Continuity

Healthcare organizations cannot tolerate disruptions to patient care that traditional security implementations often require, creating resistance to implementing proper security controls while maintaining 24/7 clinical operations across multiple hospitals and specialty clinics.​

Down_arrow
challenge-solution_icon

Elisity Solution

Phased Security Implementation

Roll out your fine-tuned policies in waves using Elisity's Simulation Mode to analyze policy impact, identify potential issues, and refine policies before full-scale deployment, safeguarding your clinical operations while strengthening security posture across your entire healthcare organization.​

See

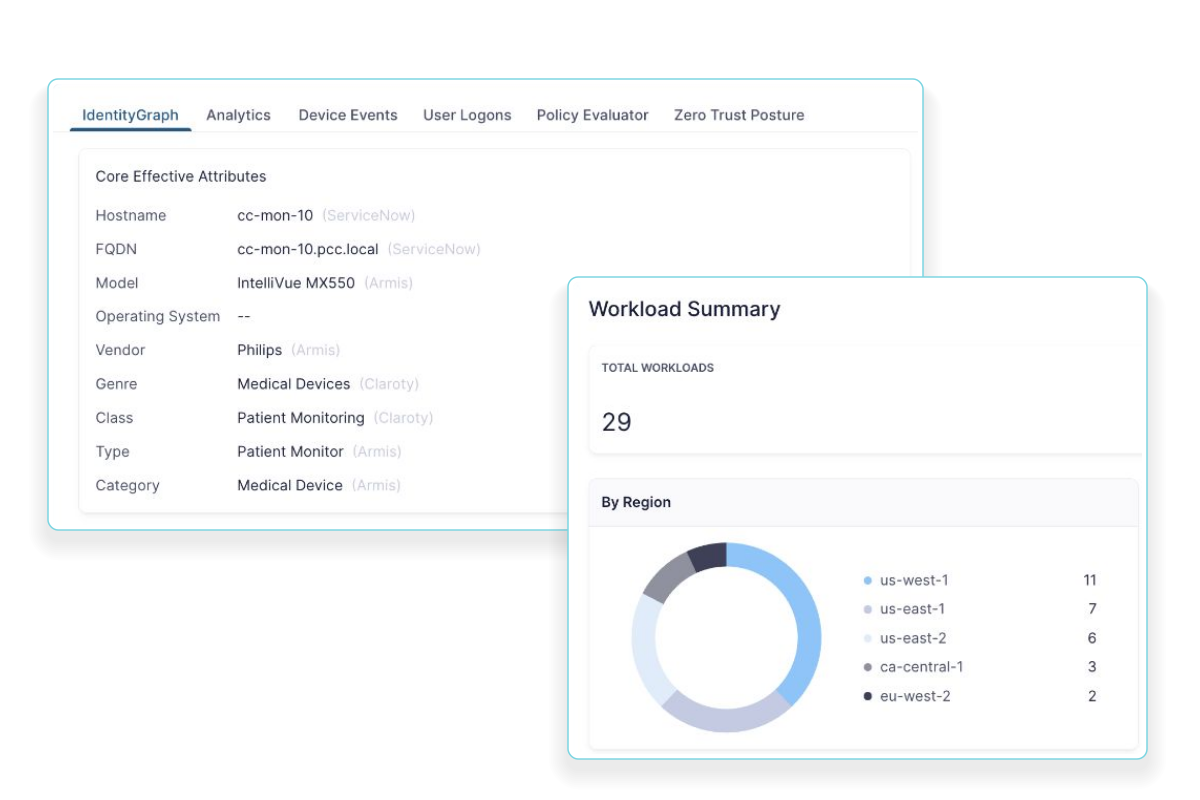
Use medical device context in policy

Bring medical device identity and connected asset context into IdentityGraph. Review observed communications before applying segmentation policy through supported network infrastructure.

Elisity IdentityGraph medical-device context alongside a cloud workload summary.

Resources

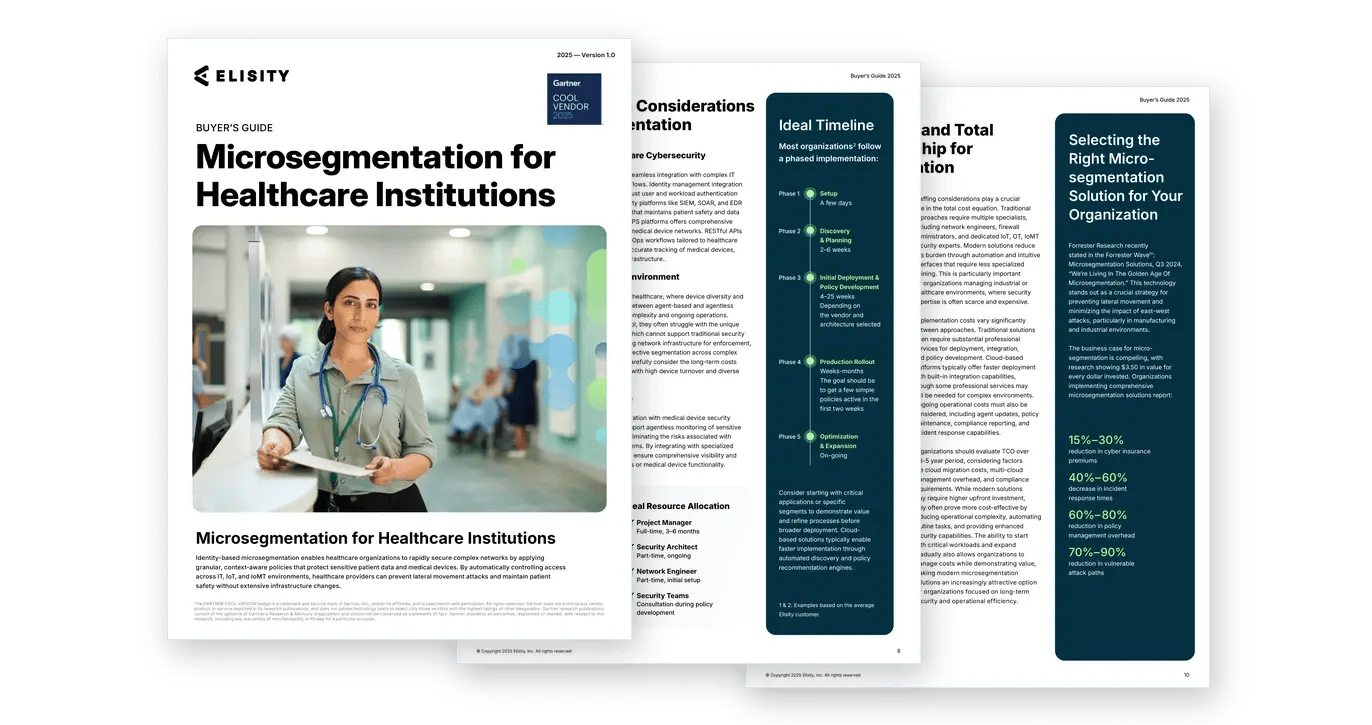
Download the Microsegmentation Buyer’s Guide and Checklist for Healthcare Organizations

An objective framework for evaluating microsegmentation against the realities of a hospital network: thousands of medical and IoMT devices that cannot run agents, 24/7 clinical operations that cannot absorb downtime, and tightening compliance mandates. Includes the questions to ask every vendor about deployment speed, clinical disruption, and time to value.

Deeper implementation detail, including HIPAA and medical device specifics, lives in Elisity’s healthcare microsegmentation guide.

Download Here
Elisity Microsegmentation Buyer’s Guide and Checklist for Healthcare Institutions, cover and interior pages

Get Started

Stop East-West Attacks, Microsegment Your Networks

Learn why and how large enterprises are reducing risks and accelerating their Zero Trust maturity with Elisity. 
Learn More

Healthcare Networks & Medical Device Security FAQ

Explore how identity-based microsegmentation helps clinical teams protect medical devices and review changes before enforcement.

Can Elisity protect medical devices that cannot run endpoint agents?

Elisity enforces access policy through supported network infrastructure, so protected medical devices do not need an Elisity software agent. Teams can limit each device to the communication needed for care and use identity and risk context to define that access.

How do healthcare teams assess policy changes before enforcement?

Teams simulate policy against observed traffic, review the effects with clinical and security owners, and activate approved policies in phases. This helps teams plan changes around patient care; it is not a guarantee of zero disruption.

How does Elisity support a healthcare compliance review?

Elisity provides asset context, segmentation policy and reporting evidence that can support a healthcare security review. The organization remains responsible for interpreting applicable requirements and validating its controls; the product alone does not establish HIPAA compliance.

Back to top
The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story
Overhead aerial of a data center campus under construction in farmland, illustrating AI agent containment architecture

The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story

14 min read
Elisity Release 26.7: Hierarchical policy, broader platform support, and deeper device context

Elisity Release 26.7: Hierarchical policy, broader platform support, and deeper device context

13 min read
AI Agent Network Security with Microsegmentation
AI agent network security: how microsegmentation contains autonomous AI agents at the network layer

AI Agent Network Security with Microsegmentation

24 min read