The Elisity platform

Identity-based microsegmentation

Connect identity and risk context across users, devices, workloads and AI agents. Simulate least-privilege policy, then enforce it through your existing network infrastructure.

Schedule Demo Download the solution brief
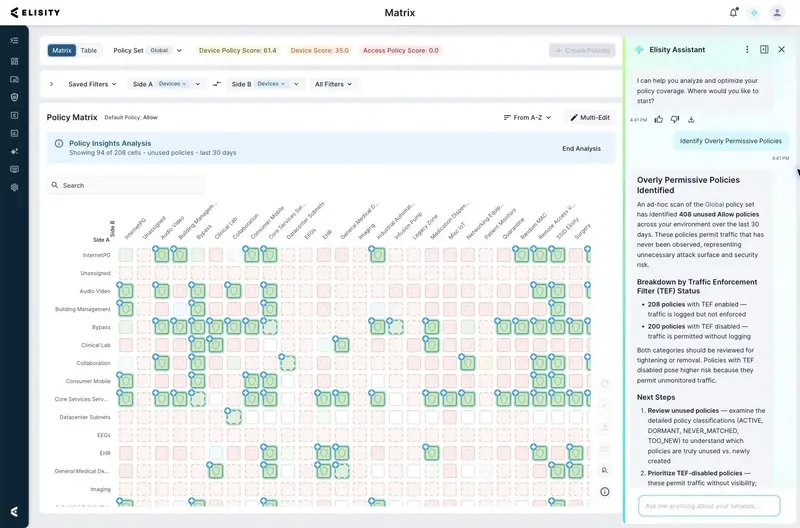
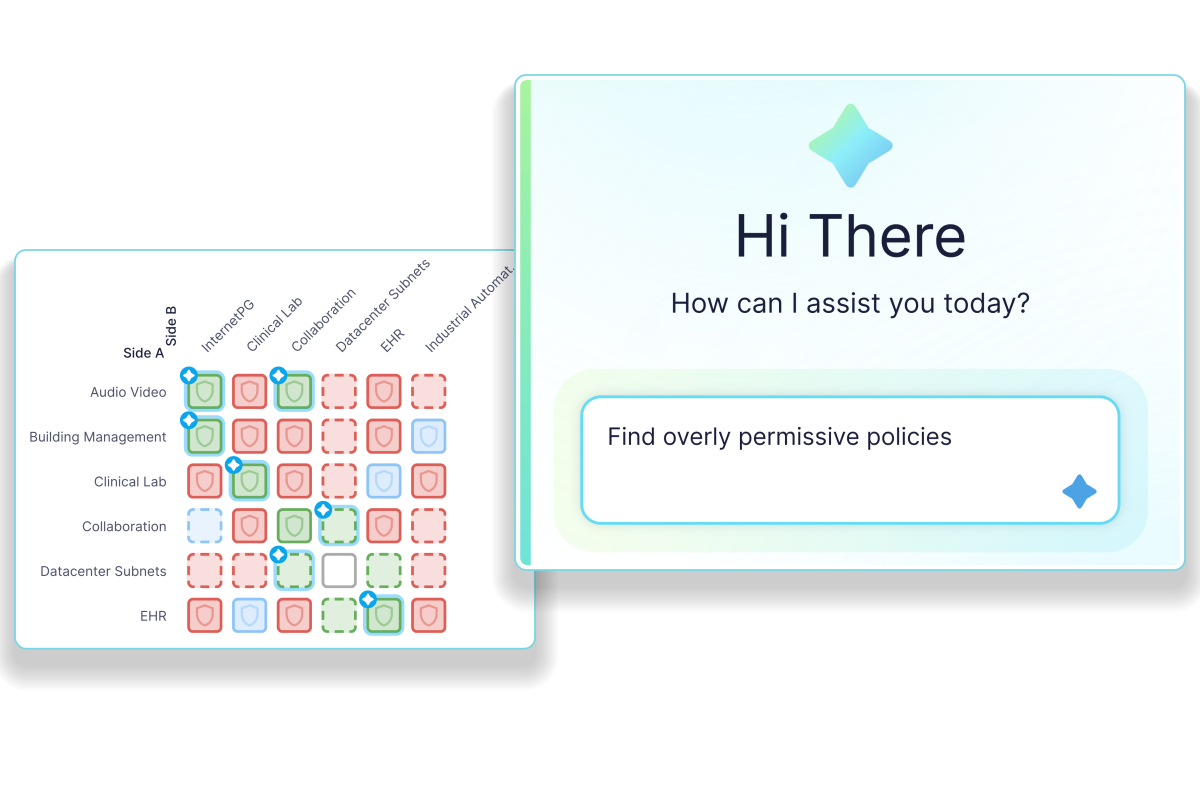
Elisity Assistant identifies overly permissive Allow policies and highlights them in the redesigned policy matrix.
St. Luke’s University Health Network logo

Customer spotlight


“Our mission was to make sure that if ransomware ever hit, it would be contained to a single asset, not take down the organization.”

David Finkelstein
CISO, St. Luke’s University Health Network

Read the May 28, 2026 release

Customer case study

See how St. Luke’s did it

St. Luke’s University Health Network

15 hospitals. 46 days.

Identity-based microsegmentation at the scale of a regional health network.

Devices
85,000
Active users
23,000
Outpatient sites
350+
Change windows
0

15-hospital rollout: Read the St. Luke’s story.

See, simulate, enforce

See

Identity across your network and cloud

  • Elisity IdentityGraph™ combines network observations with identity, endpoint, CMDB, IoT and cloud context. Bring AWS and Azure workloads into IdentityGraph alongside users and devices, with cloud tags and instance details available as policy context.
  • Apply access policy to the device or workload running an AI agent. Elisity enforces through the network, outside the agent’s runtime, without installing a software agent on the assets it protects.

In development: Elisity is extending IdentityGraph to additional non-human identities, including service accounts and machine credentials.
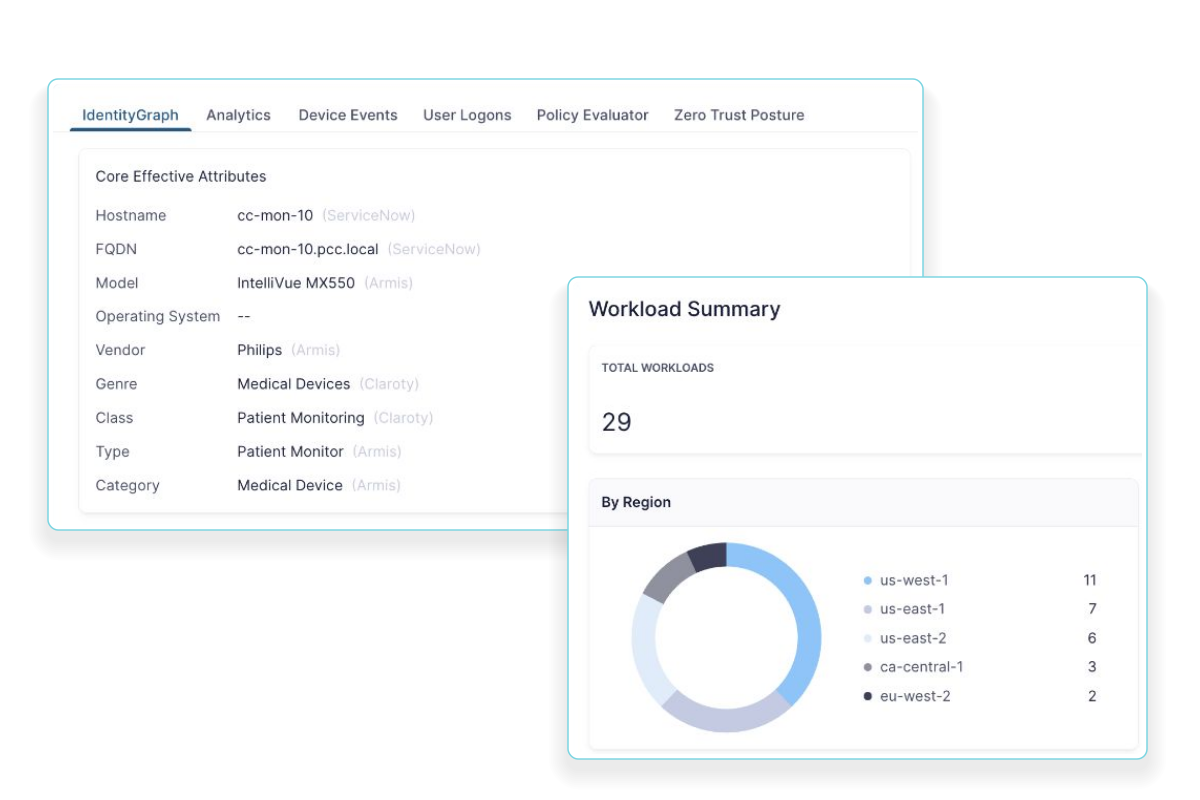
Elisity demo: device identity context and AWS workload inventory
Elisity Assistant prompt with unused Allow policies highlighted for review in the policy matrix

Decide and simulate

AI assistance. Your decision.

  • The Elisity Assistant answers plain-language questions about devices, traffic and policies inside Cloud Control Center, using live data from your tenant and scoped to each user’s permissions.
  • Elisity Intelligence proposes device classifications, Policy Groups and policies with the evidence behind each suggestion. Suggested policies start in simulation, and administrators decide what moves to enforcement.
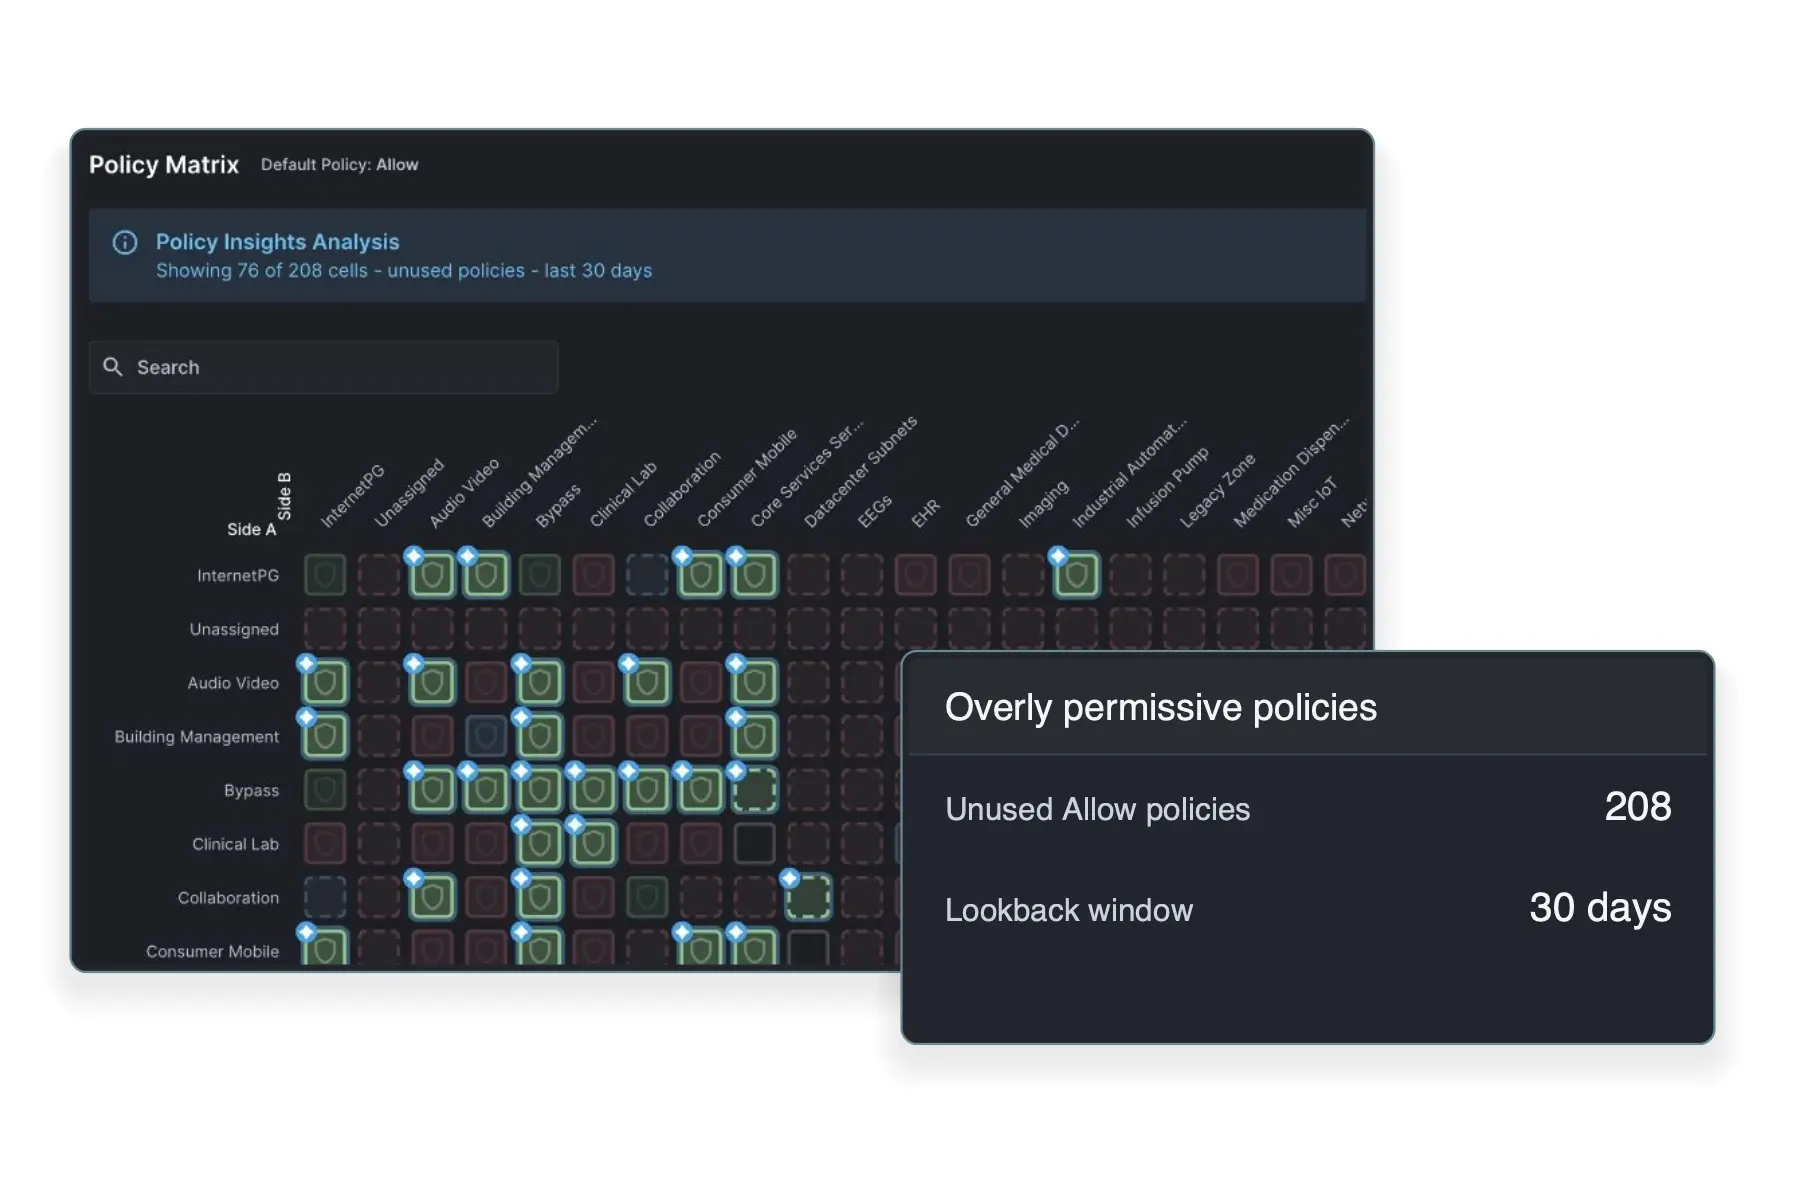
  • Elisity flags Allow policies that have carried no traffic over a review window, so teams can tighten access that no device is using.

Enforce and measure

Enforce least privilege. Measure your posture.

  • Elisity enforces identity-based policy through supported wired network infrastructure from Cisco, Arista, Juniper, HPE Aruba and Hirschmann.
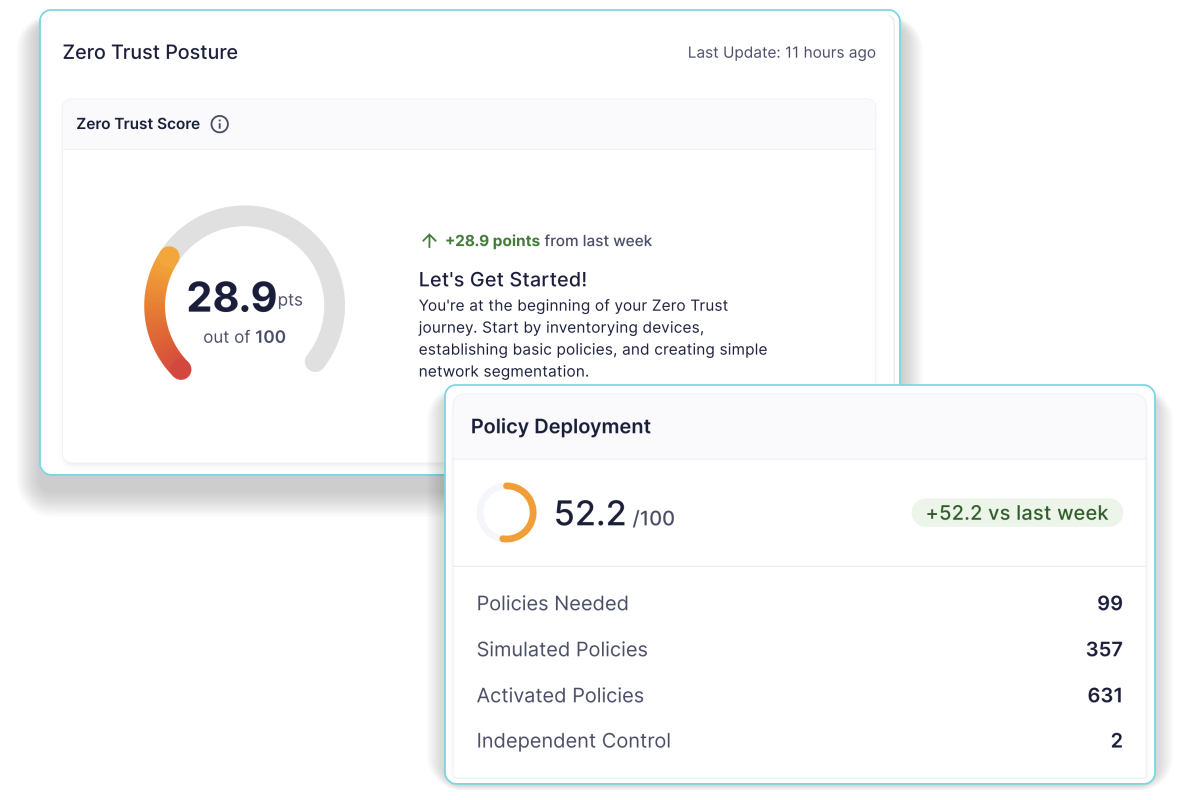
  • The Zero Trust Posture Score rates segmentation posture from 0 to 100, refreshed daily.
  • Scheduled Snapshot reports map Elisity segmentation and policy evidence to selected IEC 62443, HIPAA Security Rule and PCI DSS requirements, giving auditors documented evidence rather than a pass mark.
Elisity demo: policy deployment and Zero Trust posture factors

Inside the Elisity platform

Elisity Cloud Control Center

Elisity Cloud Control Center is the cloud-delivered console for visibility, policy and reporting, with a dedicated instance for each customer.

Elisity IdentityGraph

Elisity IdentityGraph combines network observations with context from identity, endpoint, CMDB, IoT and cloud tools to build one record per asset that policy can use.

Elisity Dynamic Policy Engine

When a connected tool changes an asset’s risk attribute, its Policy Group membership and the policy you defined follow automatically.

Elisity Intelligence

Elisity Intelligence proposes device classifications, Policy Groups and policies with the evidence behind each suggestion. Suggested policies start in simulation, and administrators decide what moves to enforcement.

Elisity Virtual Edge

The Elisity Virtual Edge connects your network infrastructure to Cloud Control Center. It sits outside the data path and programs policy into the data plane.

Any data plane

Elisity enforces identity-based policy through supported wired network infrastructure from Cisco, Arista, Juniper, HPE Aruba and Hirschmann, through Cisco Catalyst 9800 wireless controllers, and shares Policy Group membership with Palo Alto Networks firewalls as Dynamic Address Groups.

Elisity architecture: enterprise networks connect users, devices, workloads and AI agents; cloud and data center environments connect workloads, AI agents and containers. Elisity architecture: enterprise networks connect users, devices, workloads and AI agents; cloud and data center environments connect workloads, AI agents and containers.

Connect your security context

Bring identity, device and security signals into IdentityGraph. Carry that context into network policy and connect Elisity events to the tools your security team already uses.

Identity, assets and cloud

Give policy the context behind every asset.

Identity and device management

  • Microsoft Active Directory
  • Microsoft Entra ID
  • Microsoft Intune
  • 42Gears SureMDM

Asset inventory

  • ServiceNow CMDB
  • NetBox Labs

Cloud workloads

  • Amazon Web Services
  • Microsoft Azure

Security intelligence

Bring the signals your security teams trust into policy.

Endpoint and exposure context

  • CrowdStrike
  • Microsoft Defender
  • Palo Alto Cortex XDR
  • SentinelOne
  • Remedio (formerly GYTPOL)
  • Tenable Security Center

IoT, OT and medical devices

  • Armis
  • Asimily
  • Claroty xDome
  • Claroty Medigate
  • Dragos
  • Microsoft Defender for IoT
  • Nozomi Networks
  • ORDR
  • Palo Alto Networks IoT Security

Network and security operations

Connect policy enforcement with your security operations.

Network policy integrations

  • Cisco
  • Arista
  • Juniper
  • HPE Aruba Networking
  • Hirschmann
  • Palo Alto Networks firewalls / Panorama

Outbound logging

  • Splunk
  • Cribl
  • Microsoft Sentinel
  • HEC Log Exporter
  • Syslog
Explore integrations

Built for your industry

Explore the controls and customer stories that matter on your network.


Classification-1

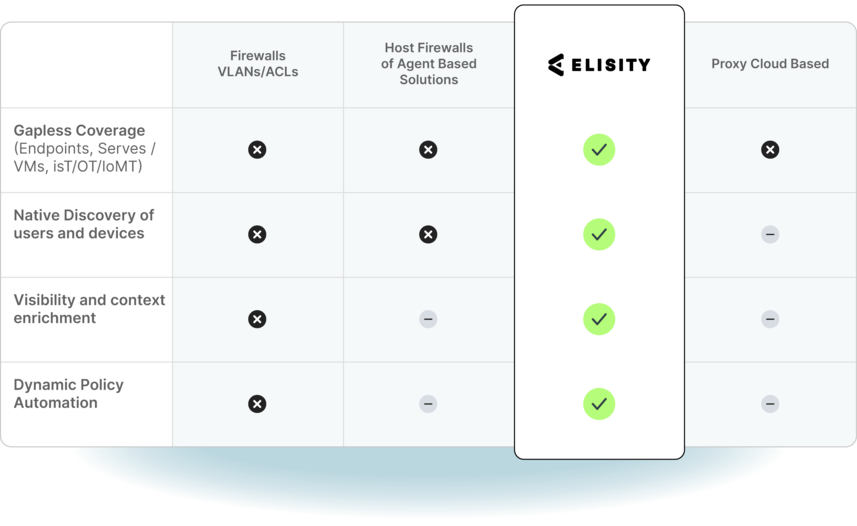
A Clear Comparison: The Elisity Microsegmentation Advantage​

Elisity microsegmentation compared with firewalls, agent-based solutions and cloud proxies across four capabilities.

What would you like to know?

Ask a question about Elisity, microsegmentation or your environment.

Powered by Claude. Answers may be inaccurate. Chats are stored and may be reviewed to improve the assistant. Please don’t share confidential information. 

See Elisity in action: Schedule a live demo

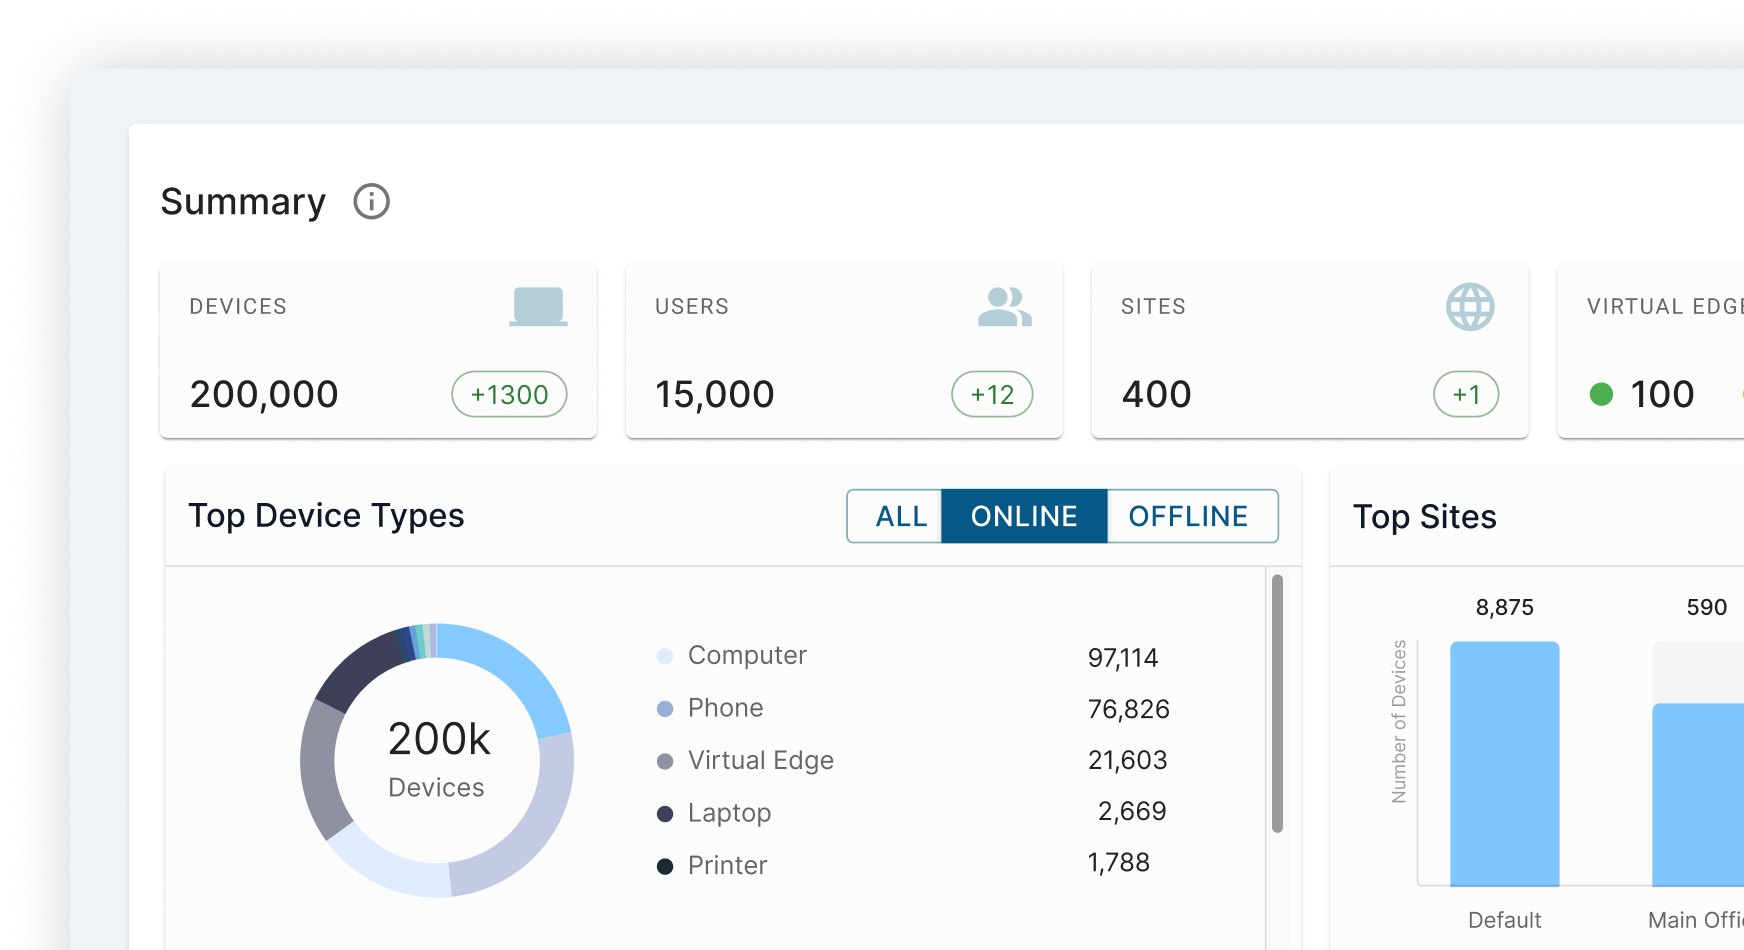
See how Elisity IdentityGraph builds one record per asset, how teams simulate policy against observed traffic, and how Elisity enforces policy through supported network infrastructure. Product UI illustration shown.

Schedule Demo
Product UI illustration of the Elisity Cloud Control Center summary dashboard

Put your policies to work

Elisity Assistant identifies unused Allow policies in the healthcare demo
Product UI detail · Based on the Elisity demo

Find overly permissive policies

Find Allow policies that have carried no traffic over a review window. Review the evidence and decide which access to tighten, helping reduce unnecessary paths through your network.

See AI policy analysis

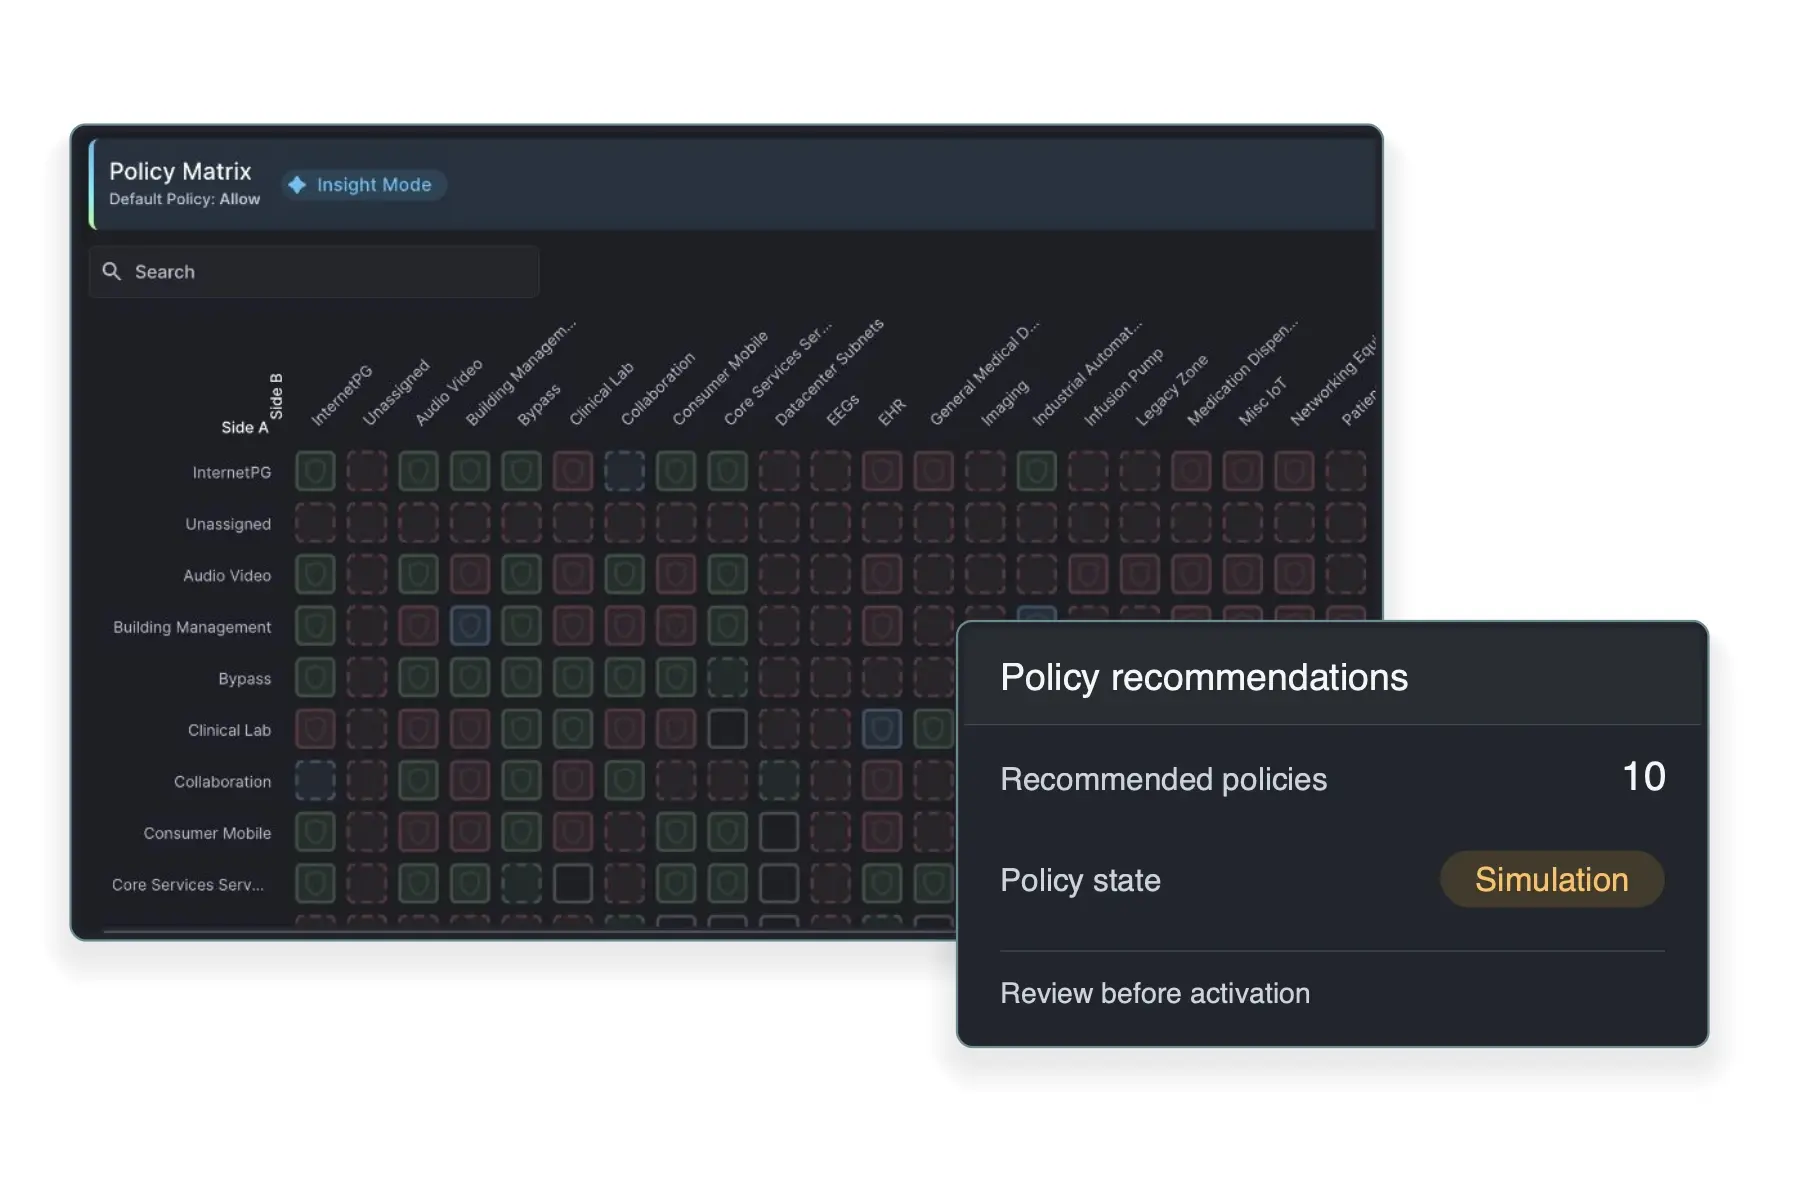
Elisity Assistant policy recommendations derived from observed demo traffic
Product UI detail · Based on the Elisity demo

Get policy recommendations

Use observed traffic and Policy Group relationships to identify policy gaps. Elisity Intelligence proposes policies with supporting context, so your team can review and refine the next step.

Explore policy recommendations

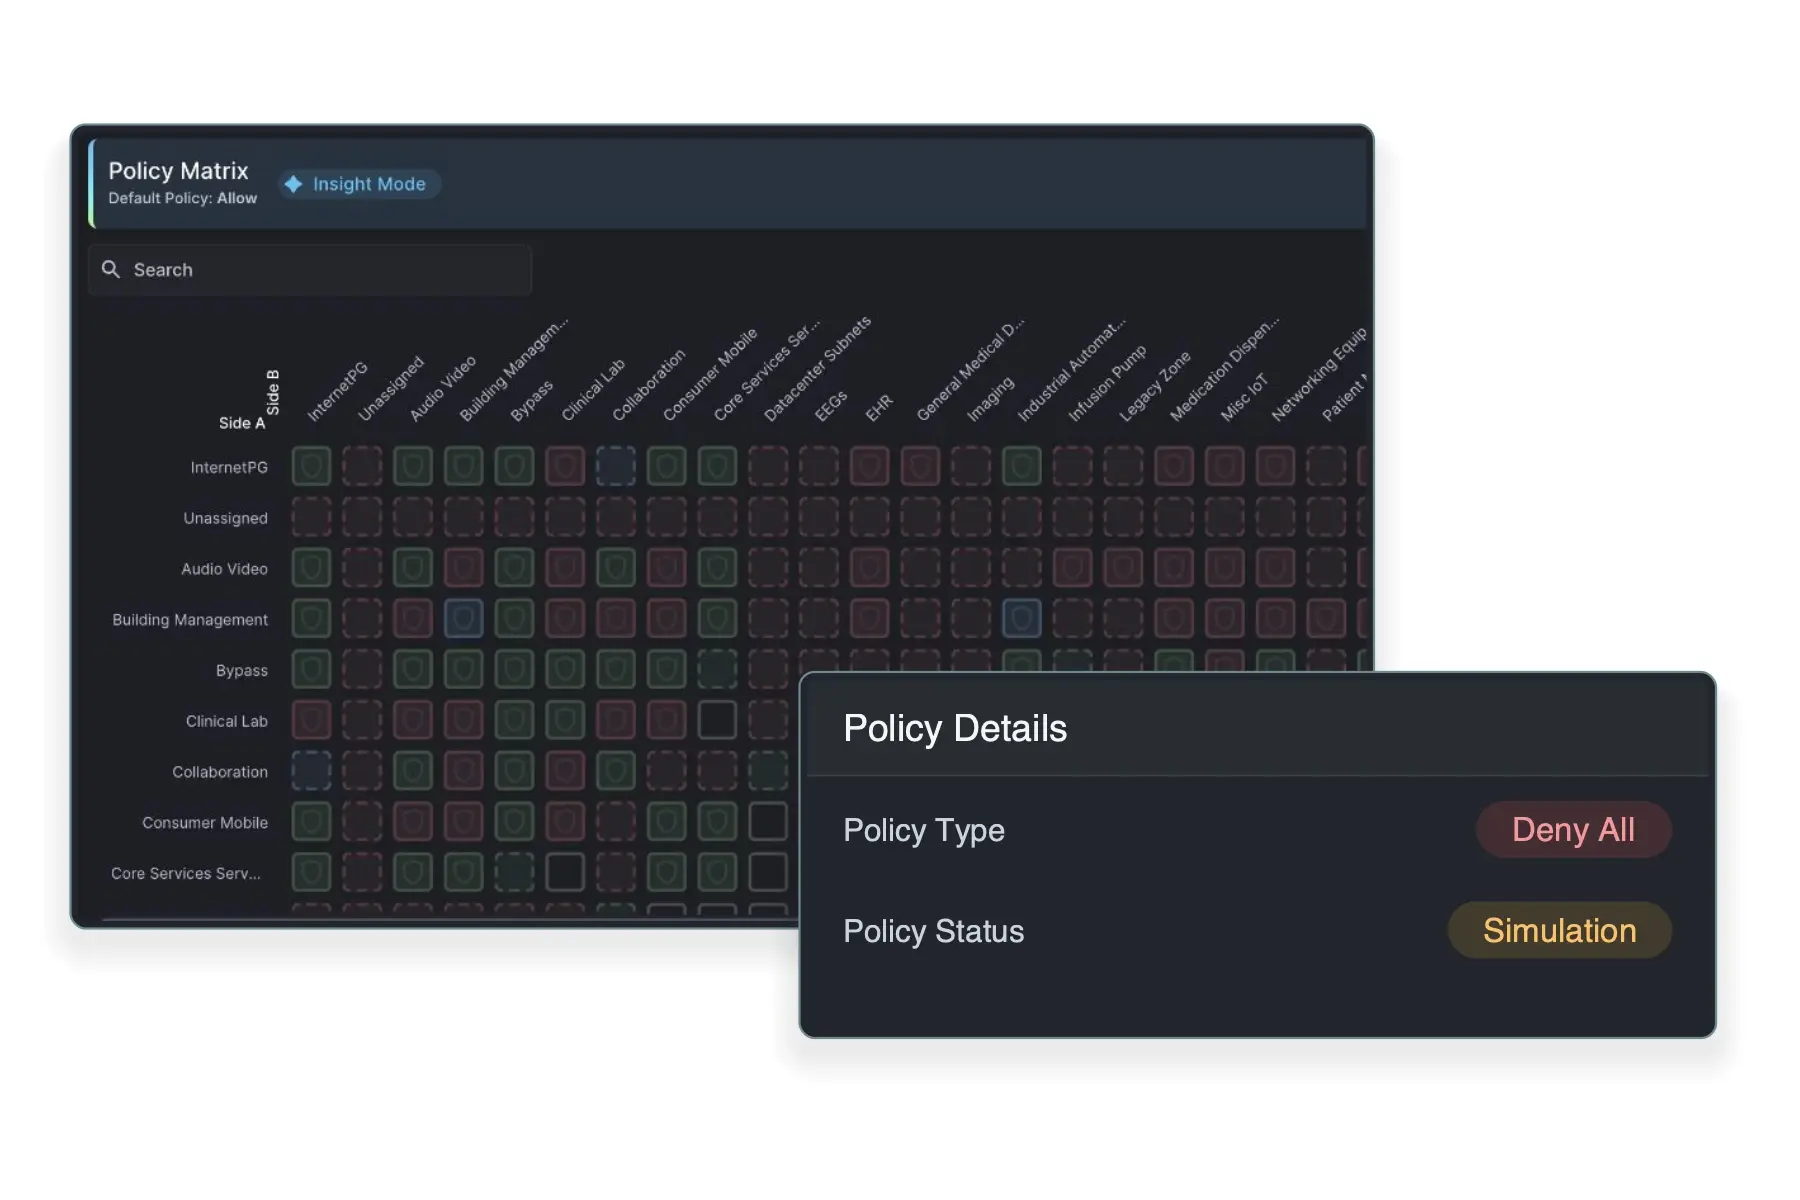
Elisity demo policy details showing Simulation status before activation
Product UI detail · Based on the Elisity demo

Review before enforcement

Suggested policies start in simulation. Assess their impact against observed traffic, refine the policy and decide what moves to enforcement. Your team stays in control of every change.

See simulation in action


The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story
Overhead aerial of a data center campus under construction in farmland, illustrating AI agent containment architecture

The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story

Aug 27, 2026, 8:15:00 AM 14 min read
Elisity Release 26.7: Hierarchical policy, broader platform support, and deeper device context

Elisity Release 26.7: Hierarchical policy, broader platform support, and deeper device context

Aug 17, 2026, 1:57:58 PM 13 min read
AI Agent Network Security with Microsegmentation
AI agent network security: how microsegmentation contains autonomous AI agents at the network layer

AI Agent Network Security with Microsegmentation

Aug 11, 2026, 11:15:00 AM 24 min read