Use Case


Zero Trust Microsegmentation

Make least-privilege access part of your Zero Trust strategy. Elisity combines identity and risk context, policy simulation and enforcement through supported network infrastructure to help contain lateral movement across users, devices and workloads.

Explore the approaches in our Zero Trust microsegmentation comparison.

Challenges

Traditional approaches to Zero Trust microsegmentation overwhelm security teams with complex hardware deployments, multiple management consoles, and extensive policy configurations. Manual discovery and classification of devices, combined with agent deployment requirements and network architecture changes, create significant operational burdens. These resource-intensive processes often lead to incomplete visibility, failed goals for implementing least privilege access policies, and delayed implementation timelines.

Place-Office

Network Segmentation Without Compromise

Transform network security with identity-based microsegmentation that enables Zero Trust in weeks, not years.
Small_Logo
Mainline-customer-spotlight-image

Customer Spotlight


“Elisity has changed how we look at microsegmentation solutions overall and we have now experienced how Elisity is the easiest to implement and easiest to manage.”

— Aaron Weismann,
CISO
Main Line Health

The Numbers

Main Line Health deploys Elisity microsegmentation enterprise-wide across their Cisco infrastructure with Armis integration, providing comprehensive protection at every facility with network presence.

6,000+

Actively Policies Enforced

+100k

IoT, OT, and IoMT Devices Protected

150

Hospitals, Health centers and physicians' practices

3

Days to Deploy

Challenge


Multiple Tools, Multiple Teams

Asset information is spread across identity, endpoint, CMDB, IoT and cloud tools. Fragmented records make it harder to understand which assets need access to each other.

Down_arrow
challenge-solution_icon

Elisity Solution


See assets in context

Elisity IdentityGraph combines network observations with context from connected tools to build one correlated record per asset. Use that identity and risk context to define Policy Groups for users, devices and workloads.

Challenge


Policies require ongoing review

As applications, devices and workloads change, access rules can become broader than necessary. Teams need evidence to review communication paths and refine least-privilege policy.

Down_arrow
challenge-solution_icon

Elisity Solution


Turn observed traffic into policy

Use observed communications to evaluate access requirements. Elisity Intelligence proposes policies for administrator review, and simulation helps teams assess the effect of a change before they activate it.

Challenge


Critical services need careful changes

Segmentation changes can affect essential business services. Teams need a phased rollout with visibility into required traffic and a clear review process before enforcement.

Down_arrow
challenge-solution_icon

Elisity Solution


Simulate, enforce and measure

Simulate proposed policy against observed traffic, review the results, and choose what moves to enforcement. Track policy deployment and Zero Trust posture as you refine access through supported network infrastructure.

Enforce and measure

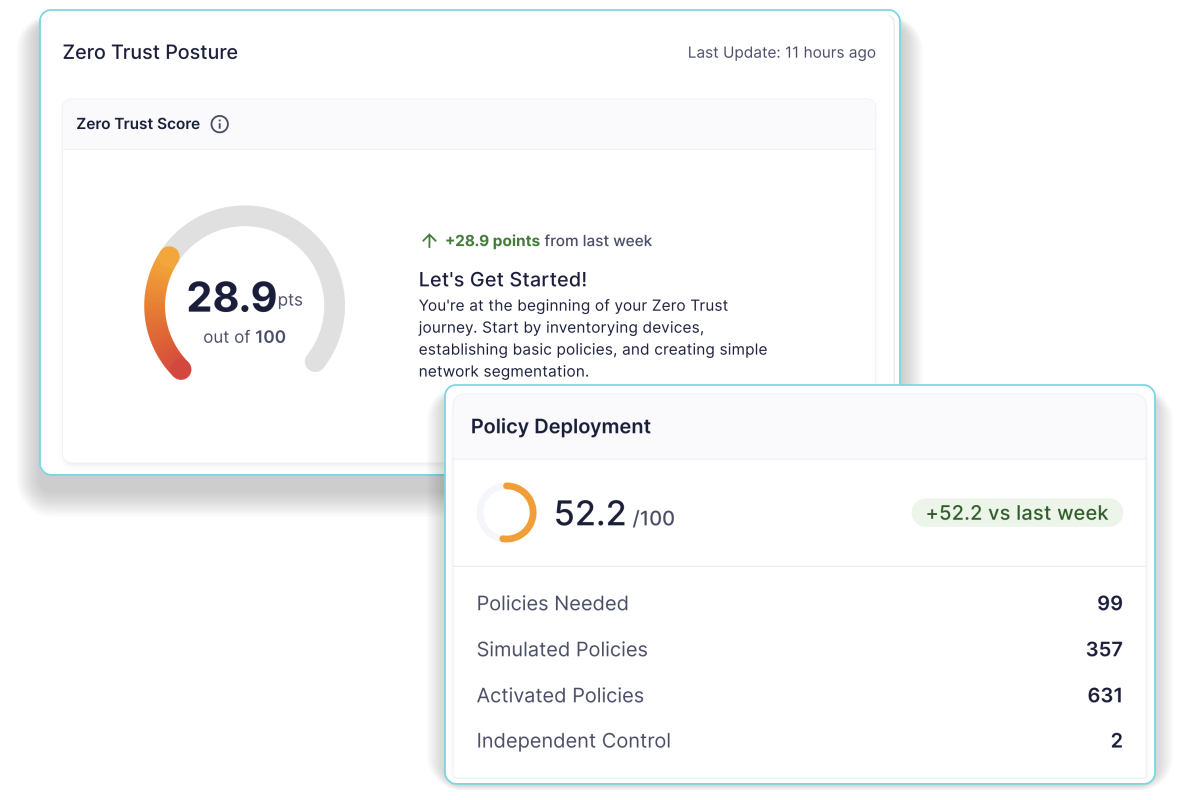
Track your segmentation progress

Review Zero Trust posture and policy deployment in one place. Use the evidence to prioritize the next policy changes and measure progress as reviewed policies move into enforcement.

Elisity Zero Trust posture score and policy deployment measures.
Get_Start_Eyebrow

Stop East-West Attacks, Microsegment Your Networks

Learn why and how large enterprises are reducing risks and accelerating their Zero Trust maturity with Elisity. 
Learn More

Resources


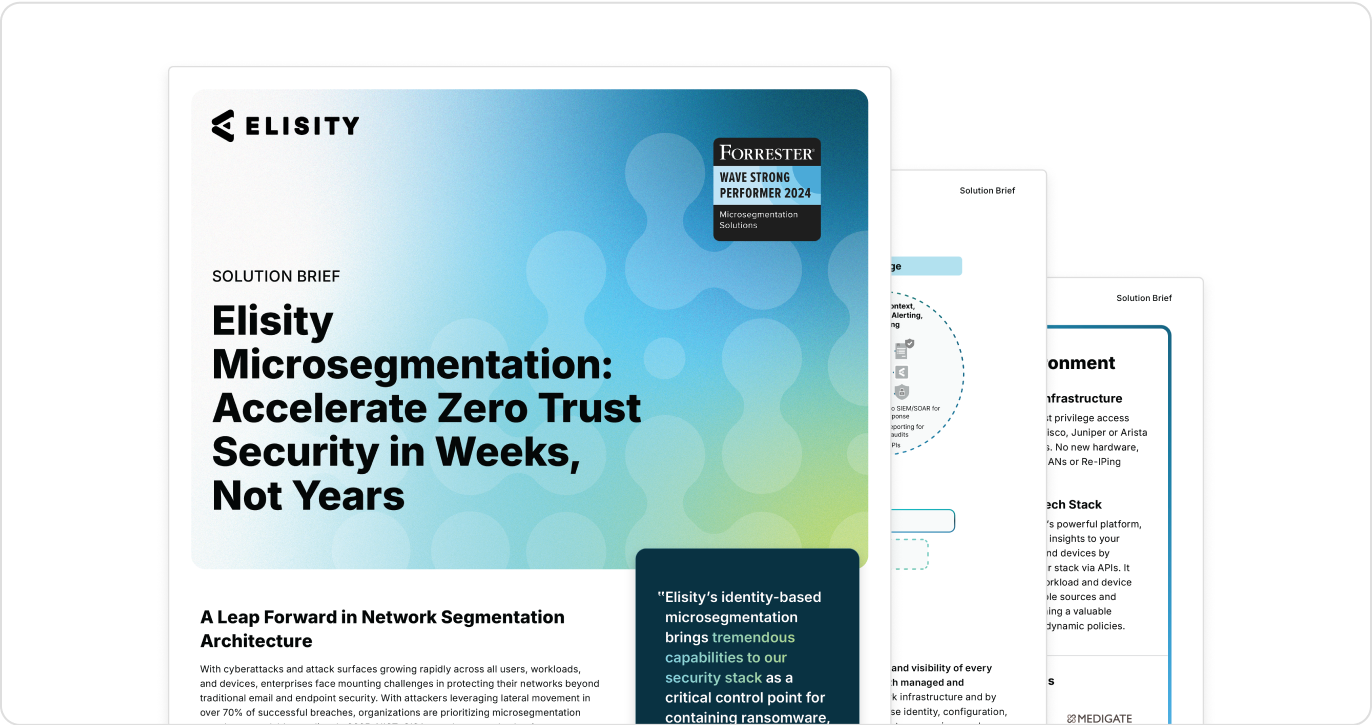
Elisity Microsegmentation: Accelerate Zero Trust Security in Weeks, Not Years

Download and discover a leap forward in network segmentation architecture.

Zero Trust Microsegmentation FAQ

Ready to accelerate your Zero Trust architecture strategy? Get answers to common questions about how Elisity simplifies microsegmentation and enforces least privilege access across all users, devices, and workloads.
How does microsegmentation support Zero Trust?

Microsegmentation limits communication between assets to the access they need. It supports a Zero Trust strategy by applying least-privilege network policy; it does not replace every other Zero Trust control.

How does Elisity use our existing infrastructure?

Elisity programs policy into supported network infrastructure. Virtual Edge operates outside the data path, and the protected asset does not need an Elisity endpoint agent. Check current hardware and software compatibility when planning deployment.

How do we review a policy before enforcing it?

Use simulation to assess a proposed policy against observed traffic. Administrators review the results and decide which policies move to enforcement. Use the results to refine access and plan a phased rollout.

Can cloud workloads contribute to policy context?

AWS and Azure connectors bring workload tags and instance details into IdentityGraph alongside users and devices. Visibility into a workload is distinct from where network policy can be enforced; confirm the supported enforcement design for your environment.

Back to top
The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story
Overhead aerial of a data center campus under construction in farmland, illustrating AI agent containment architecture

The OpenAI Hugging Face Incident Is a Lateral Movement Story, Not a Rogue AI Story

14 min read
Elisity Release 26.7: Hierarchical policy, broader platform support, and deeper device context

Elisity Release 26.7: Hierarchical policy, broader platform support, and deeper device context

13 min read
AI Agent Network Security with Microsegmentation
AI agent network security: how microsegmentation contains autonomous AI agents at the network layer

AI Agent Network Security with Microsegmentation

24 min read
See Elisity on your network

See how Elisity builds asset context, simulates policy against observed traffic and enforces least-privilege access through supported network infrastructure. Schedule a live demo around your environment.
Elisity_White